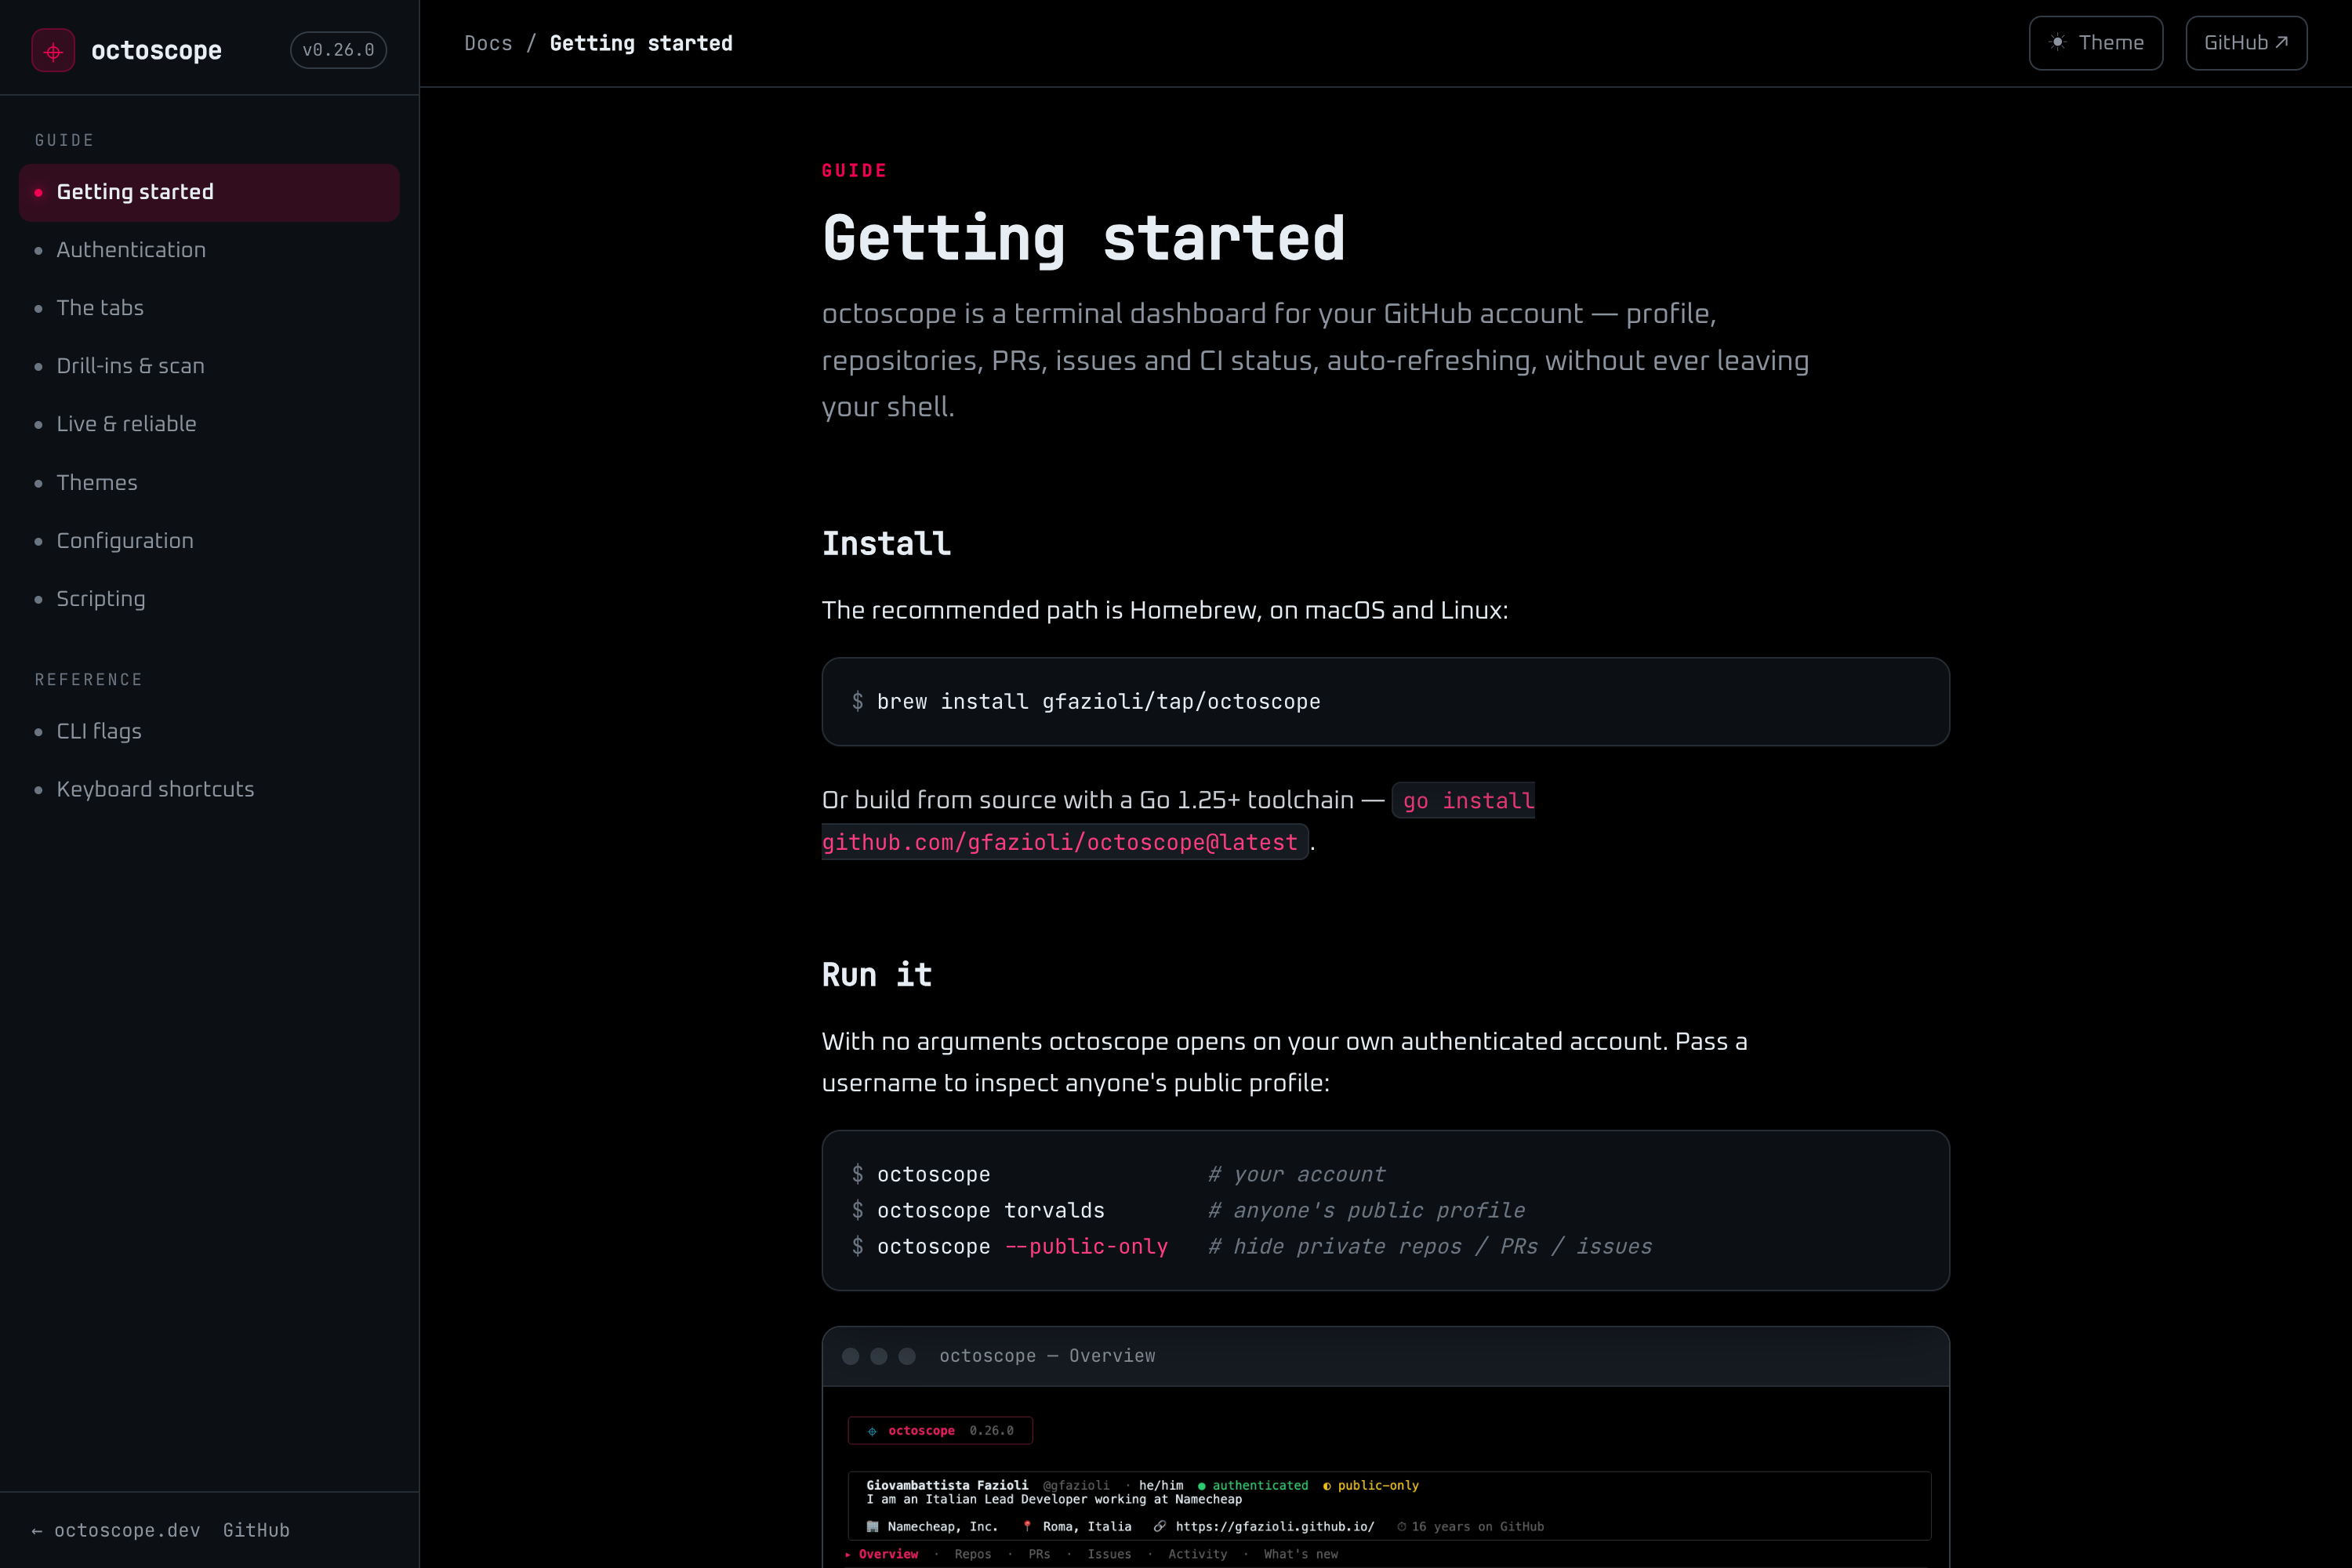
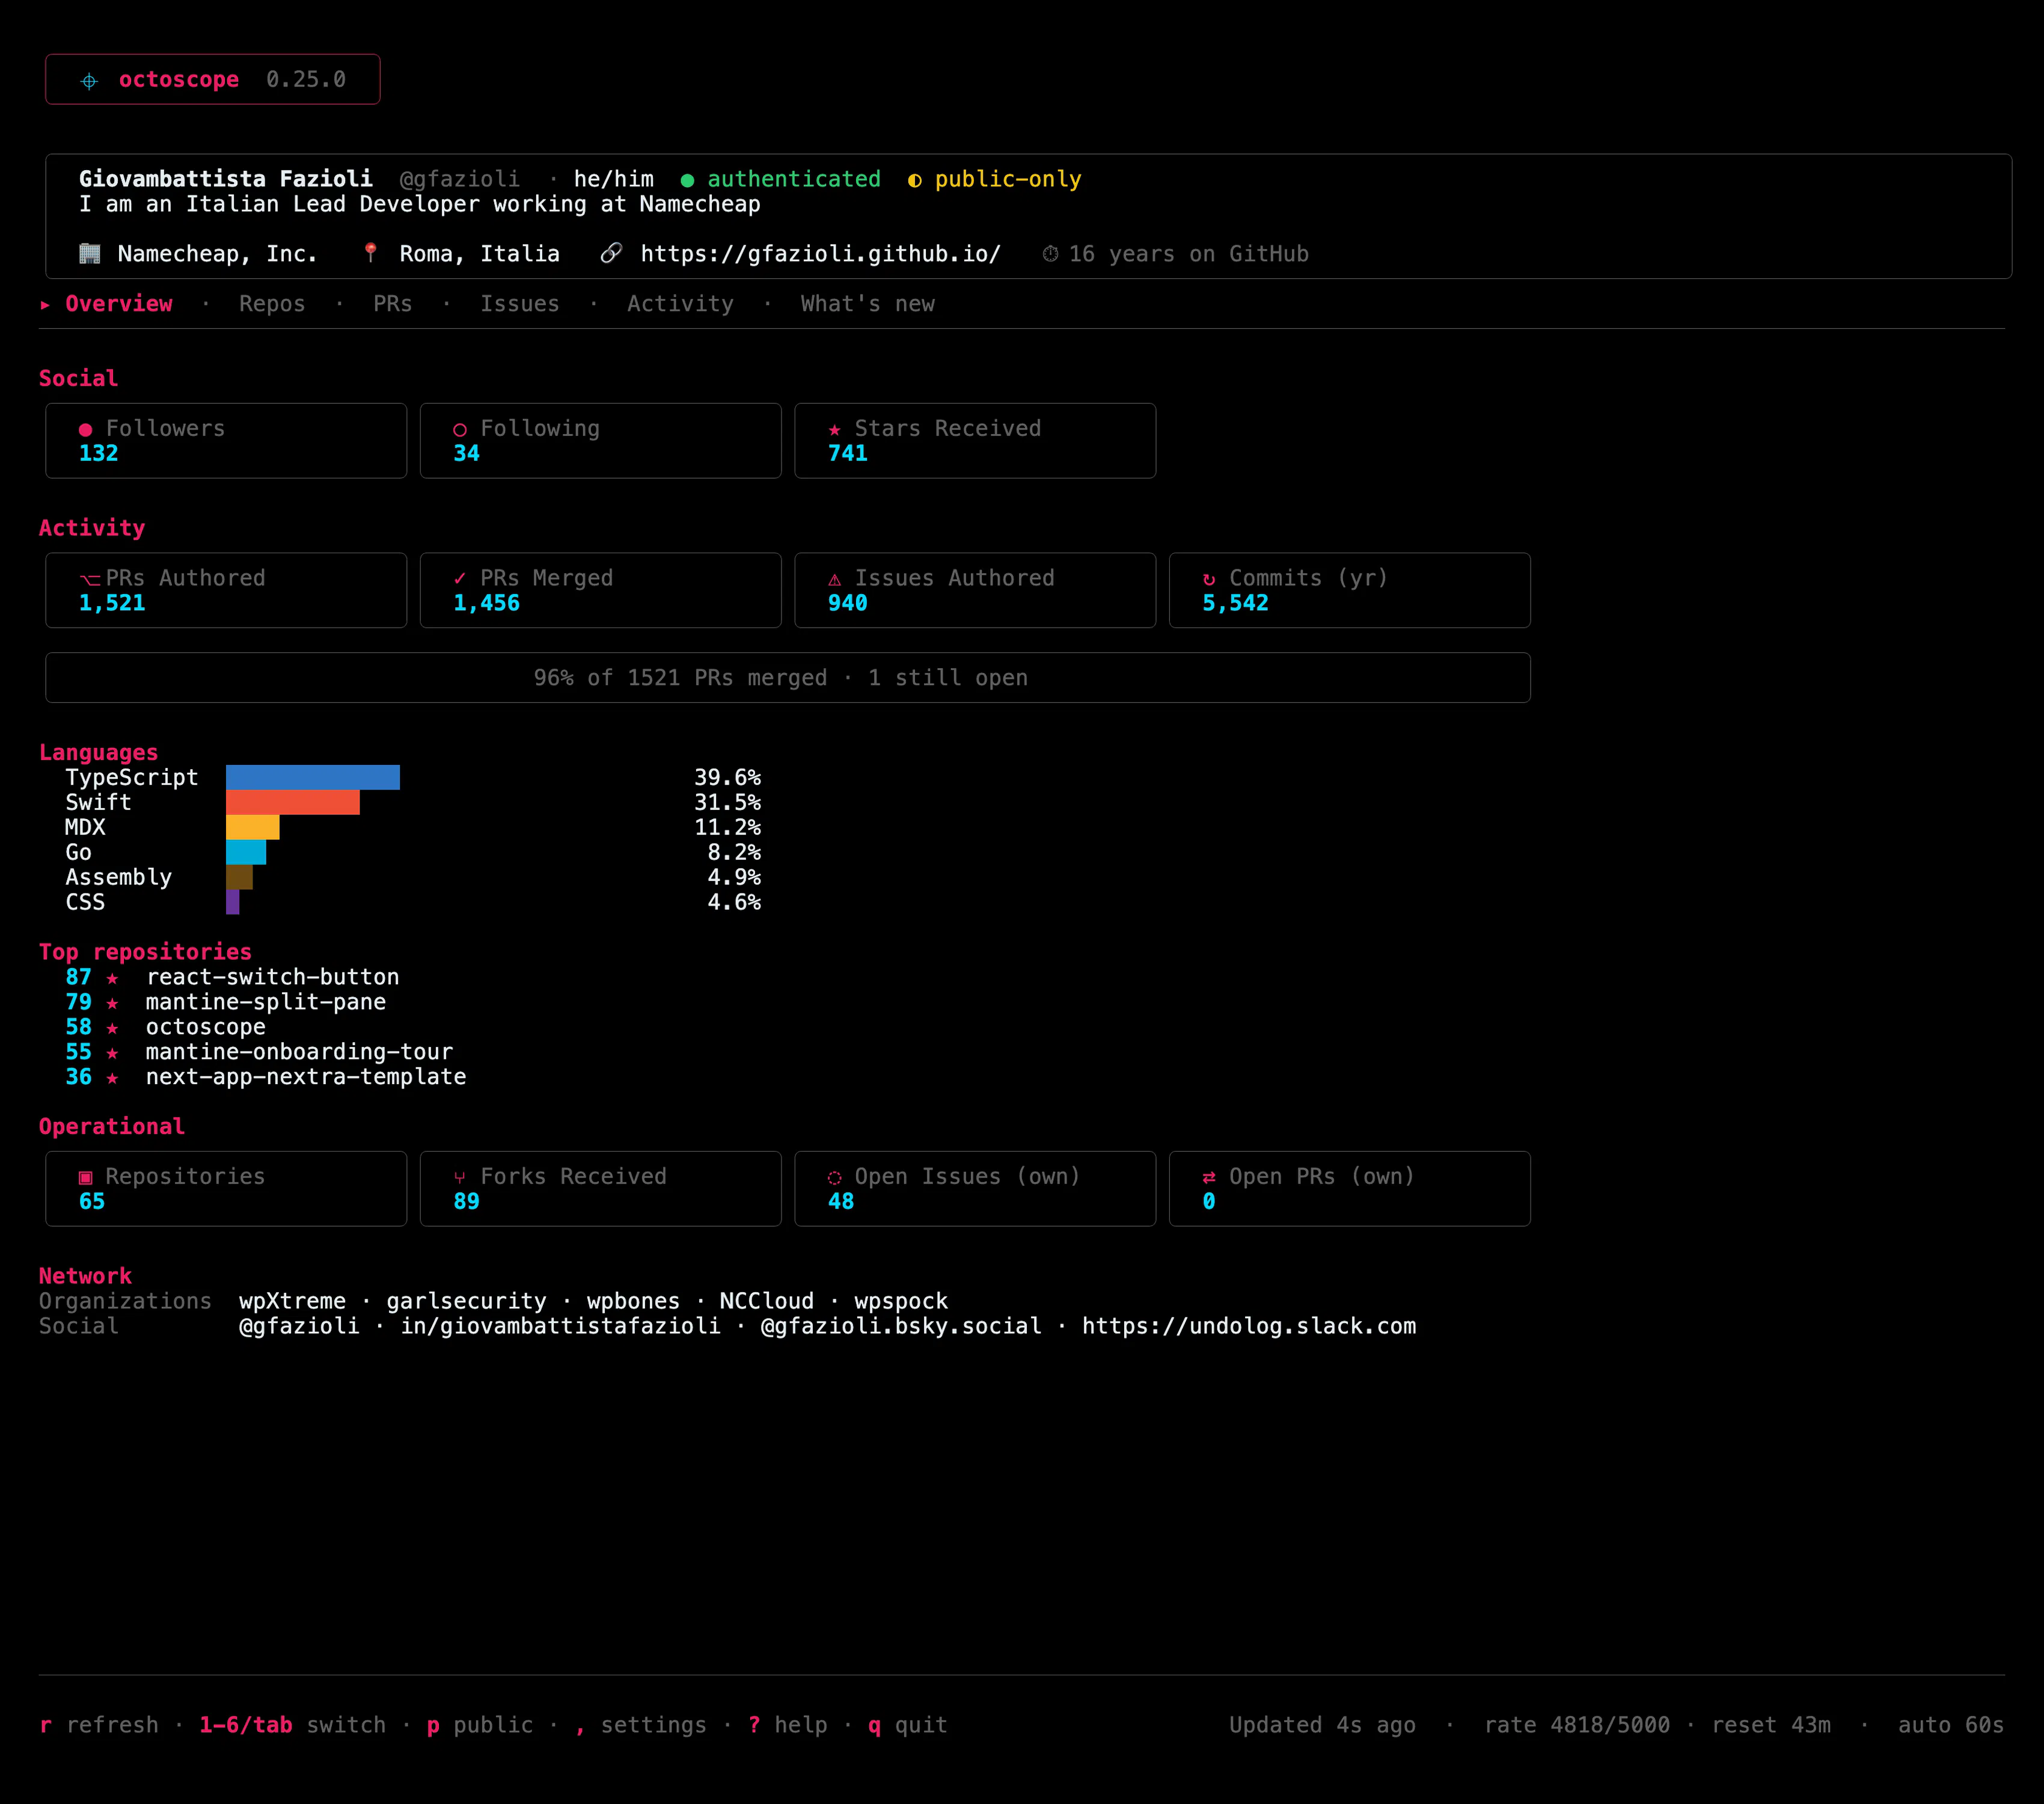
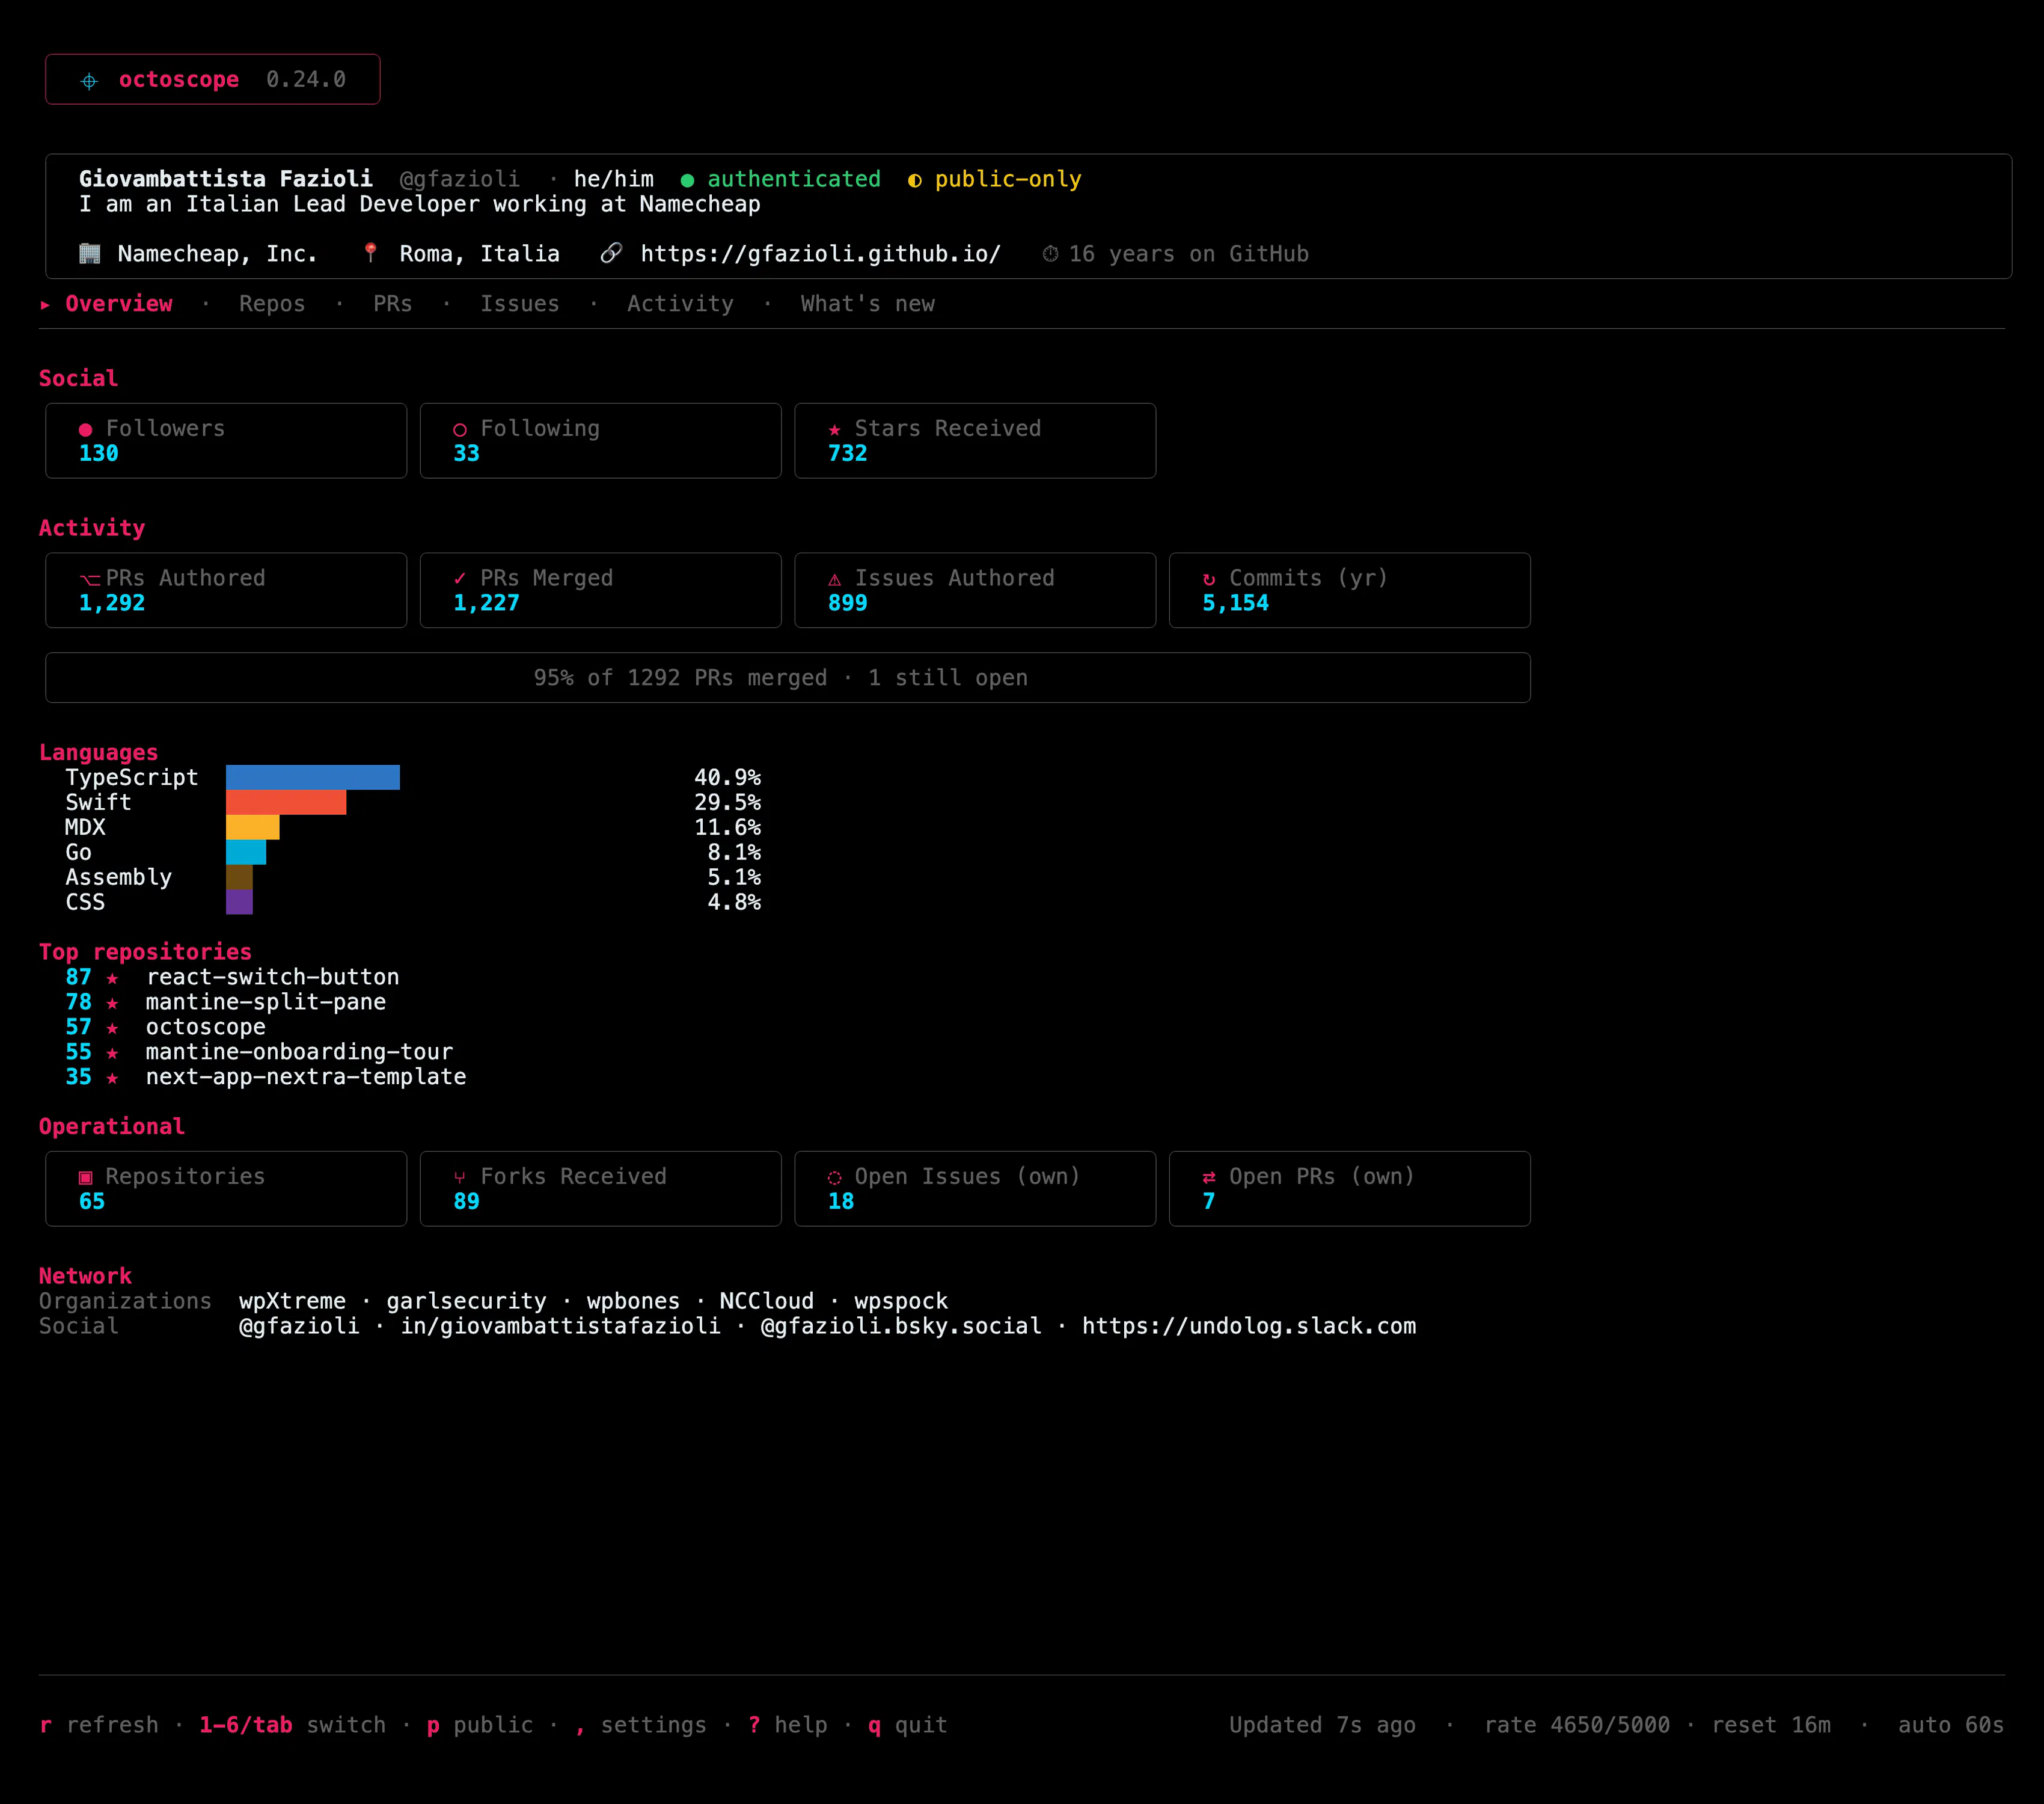
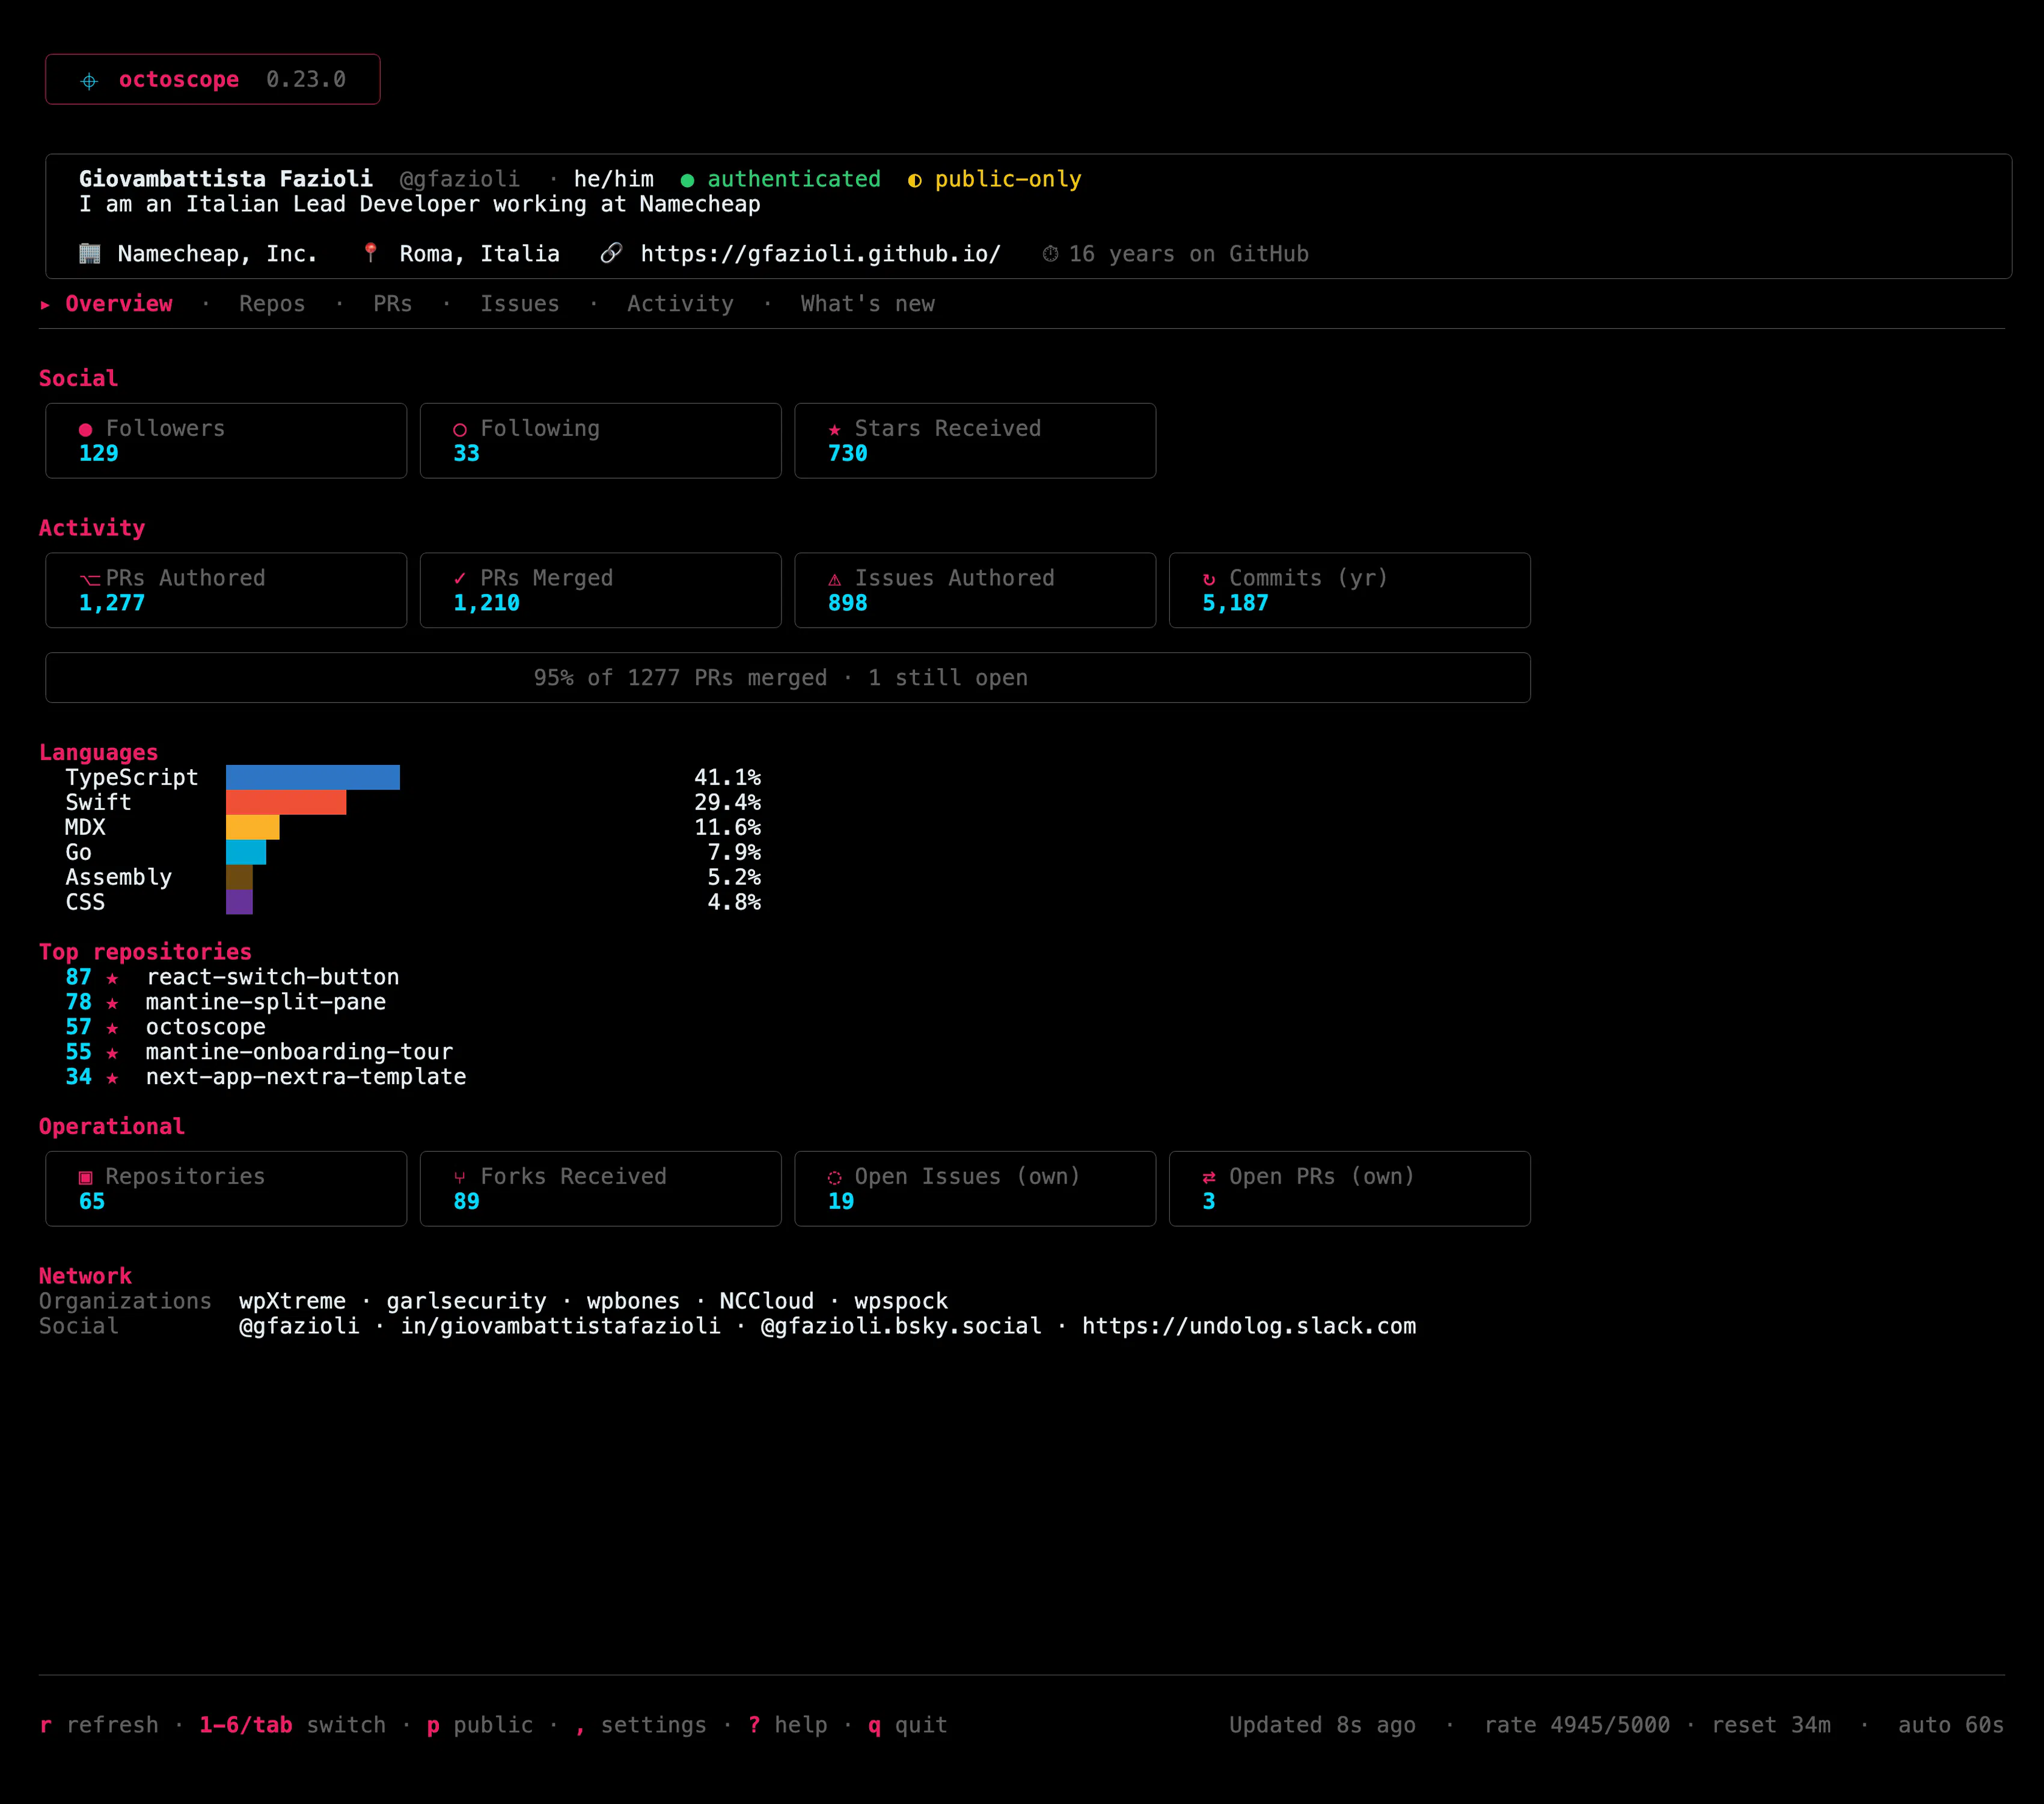
The big one first: octoscope has a real guide now. Ten pages at its own address Getting started, Authentication, The tabs, Drill-ins & scan, Live & reliable, Themes, Configuration, Scripting, plus a reference pair for every CLI flag and every keybind. https://gfazioli.github.io/octos...
The Repos tab has shown a CI rollup dot per repository for a while, and it always stopped there. Red meant something was wrong, and then you went to the browser to find out what. That last step was the annoying one.
Now you open the repo and the drill-in answers it: a Checks section listing the individual checks on the default branch, with failures floated to the top. That ordering matters more than it sounds the list is capped at eight rows, so a red job in a forty-job matrix would otherwise hide behind all the passing ones.
No new tabs this time three small read-only features that answer questions you'd normally leave the terminal for: how a repo's stars are really trending, how much API budget you've actually got left, and which of your repos need attention right now.
No new tabs this time. v0.17.0 is the boring-on-purpose release: I went back through everything you actually touch in a long session and made the app meaningfully steadier underneath. It does the same things v0.16.0 did it just behaves the same in hour eight as in minute one.
Sponsor splash a gentle nudge at launch to support development. Press o to open the Sponsors page, c to copy the link, any other key to dismiss. Suppressed under --public-only; opt out with show_sponsor=false or --no-sponsor.
"What's new" tab (press 6) the highlights of the version you're running, bundled into the binary so it works offline, with a link to the full release notes.
The Shai-Hulud / Miasma worm has been quietly pushing itself into people's GitHub repos including real, well-known OSS projects where it auto-runs the moment you open the repo in an AI editor (Claude / Cursor / Gemini / VS Code) or install it, then harvests your tokens. It lives in the GitHub source, not the npm registry, so a lockfile audit never sees it. octoscope already points at the repos you own, so this release teaches it to look. @icflorescu
What it catches
On a Repos row, open the action menu (space) and hit Security scan (s). It matches the invariant of the attack instead of a single payload filename because the worm renames its dropper the week after you blocklist it, so a renamed variant still trips it.