
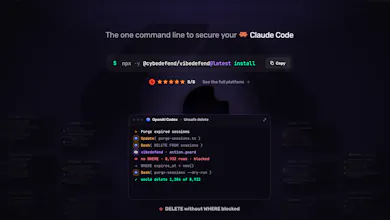
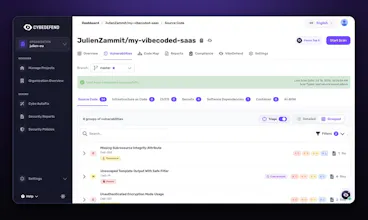
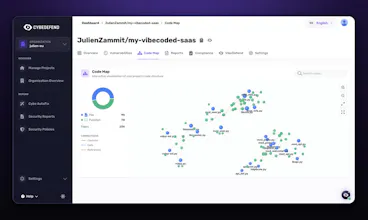
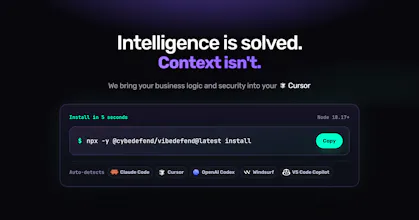
CybeDefend secures the code your AI agent writes, from inside the agent. One command installs VibeDefend on Claude Code, Cursor, Windsurf, Copilot, Codex and other agents. The agent then codes with your business rules, mined from your repo, and your security rules in its context. Each diff is scanned while the file is open, and a guard stops rm -rf, sudo or secret reads before they run. SAST, SCA, secrets, IaC, CI/CD and container scanning are included. Free plan, no card.
This is the 2nd launch from CybeDefend. View more

VibeDefend by CybeDefend
Launched this week
VibeDefend installs on your AI coding agent (Claude Code, Cursor, Windsurf, Copilot, Codex and more) with one command. From then on the agent writes with your business rules, mined from your repo, and your security rules in its context. It scans each diff while the file is still open, and a guard refuses rm -rf, sudo or a read of your secrets before it runs. Scanners check code after the commit, this runs before the line is written. Free plan, no card.
Free Options
Launch Team / Built With


From reading the origin story to the "all the apps I scanned were hackable in five minutes" quote, I was left thinking about how this is probably true of many repositories that I have worked with myself. Since there is no card required, this would be my first place to try it out, without the purchase discussion.
CybeDefend
@julien_zammit @florentin_ledy and @axel_paulin good start and it says something about your confidence in the product when all of you are responding to comments with actual facts rather than talking points. The line I found compelling was "the rule you never wrote down" as this is the true failure case for most teams, not the vulnerability that is scanned for.
CybeDefend
@dhiraj_roy1 Thanks for noticing! We built this for engineers, so facts over fluff is our baseline.
You nailed the exact problem. Standard tools catch standard bugs. The real danger is the implicit business logic living only in a senior developer's head. Agents fail hard there because they lack context.
This is why our repo miner extracts those unwritten rules and turns them into hard boundaries before the agent even starts coding.
CybeDefend
BuildShip
great to have new security products in the devtools space. I love that you have dedicated comparison pages for existing tools - really easy to differentiate. kudos on the launch!
Mastra
are you using existing security tools already? would love to know more about your experience
Mastra
also curious what's your preferred AI coding agent? anything they did that scared you lately?
CybeDefend
@mufassir_kazi Glad they help! They mostly answer one question, and the honest answer is that you keep the scanner you already run and add the part that lives inside the agent, the rules before each edit and the guard on each tool call. They're all here for the side by side: cybedefend.com/en/compare
CybeDefend
Hey Product Hunt 👋 Florentin, one of the three co-founders with Julien and Axel. I lead product vision and tech.
Quick one from the tech side. The bugs that scare me most in AI-written code aren't injections, scanners already catch those. It's the agent happily shipping an endpoint where user A can read user B's data, because nobody ever told it that rule. That's why VibeDefend mines your business rules from your repo and puts them in the agent's context before it writes.
Testing it takes a couple of minutes and it's free, no card needed. If you go further, WELCOME50 gets you 50% off your first month: cybedefend.com
And please, tell us everything: what you love, what annoys you, what's missing. We genuinely love collecting feedback and shaping the product around what you actually need.
@cybedefend @florentin_ledy If this actually works as seamlessly as describe it’s a total game changer for our workflow. congrats team for second launch🙌
Mastra
yes, it does! one command line to secure your AI coding agent -- @Cursor, @Claude Code, or else:
CybeDefend
@priya_kushwaha1 Thank you Priya! This one is about a single idea the agent already knows how to code, what it lacks is your context, the rules that live in your repo and in your engineers' heads. If you try it on one project, tell us which rule it caught first, that's the story we love hearing :) If you want the five-minute version first: cybedefend.com/en/blog/secure-app-in-5-minutes-ai-agent
Mastra
this 👆 and friendly reminder: testing @CybeDefend takes a couple of minutes, it's free, no card needed, and if you go further, WELCOME50 gets you 50% off your first month.
cybedefend.com
CybeDefend
Hey Product Hunt 👋
I'm Julien, one of the three co-founders of CybeDefend with Florentin and Axel. We're in our mid-twenties and we started the company in Lille in January 2025. Every vibe-coded app I scanned was hackable in five minutes, and that is the problem we work on every day.
The idea we started with is that security should speed you up, not stand in your way. AI agents now ship thousands of lines a day and a human can't read all of it, so we moved the check to the place where the code gets written.
VibeDefend plugs into your agent with one command. It gives the agent your business rules, mined from your repo, and your security rules before it writes a line, scans each diff while the file is still open, and stops rm -rf, sudo or a read of your secrets before they run.
We want every line an AI agent writes to already follow your rules, including the ones you never wrote down.
It's free to start, no card: cybedefend.com
Tell me what your agent did last week that scared you, I'm here all day to answer!
Mastra
The State of Vibe Coding 2025 report [1] highlighted 3 types of vulnerabilities: exposing secrets, access misconfigurations, hardcoded credentials. Do you share this opinion? or have you found more patterns based your user interviews and research?
[1] The State of Vibe Coding 2025 in /p/vibecoding
CybeDefend
@fmerian Those three for sure, and secrets are the easiest to stop, the guard refuses the read of a .env before the value ever reaches the agent's context. I'd add the rule that only lives in someone's head, like 'an invoice can't be edited once it's sent', where the code is clean and every scanner passes it. That one has to reach the agent before it writes the endpoint, which is what we built VibeDefend around. More on that family of bugs: cybedefend.com/en/blog/business-logic-flaws-ai-generated-code
As I went through the review posted by Olivier, what caught my attention was the fact that his criticism about how UI still requires many clicks for manual resolution is actually far more valuable than all the fluff written in the review; this is because he actually uses the software on a daily basis.
CybeDefend
CybeDefend
PaymentKit
The rm -rf and secrets guard is what really sealed the deal for me. All other tools scan after the problem happens; this stops it in its tracks. Today’s product would really enable us to reach the right people.
CybeDefend
CybeDefend
@hamza_aafzal Out of curiosity, which coding agents (Cursor, Claude Code, etc.) are you currently experimenting with ?