
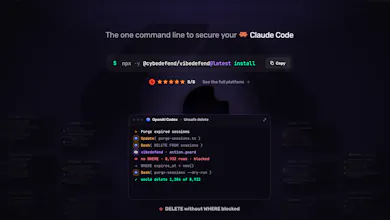
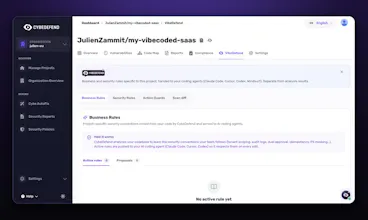
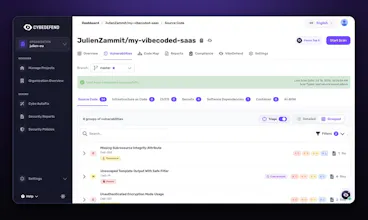
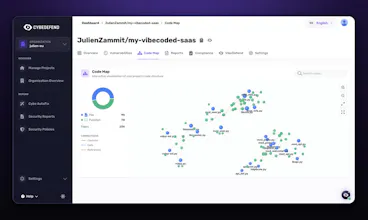
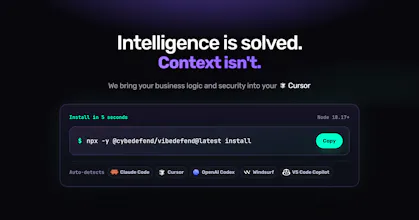
CybeDefend secures the code your AI agent writes, from inside the agent. One command installs VibeDefend on Claude Code, Cursor, Windsurf, Copilot, Codex and other agents. The agent then codes with your business rules, mined from your repo, and your security rules in its context. Each diff is scanned while the file is open, and a guard stops rm -rf, sudo or secret reads before they run. SAST, SCA, secrets, IaC, CI/CD and container scanning are included. Free plan, no card.
This is the 2nd launch from CybeDefend. View more

VibeDefend by CybeDefend
Launched this week
VibeDefend installs on your AI coding agent (Claude Code, Cursor, Windsurf, Copilot, Codex and more) with one command. From then on the agent writes with your business rules, mined from your repo, and your security rules in its context. It scans each diff while the file is still open, and a guard refuses rm -rf, sudo or a read of your secrets before it runs. Scanners check code after the commit, this runs before the line is written. Free plan, no card.
Free Options
Launch Team / Built With


CybeDefend
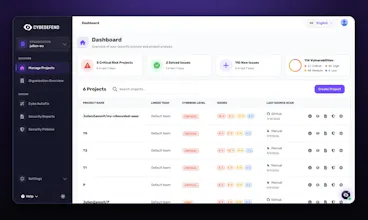
Thanks Olivier! Fair point on the clicks, it goes straight to the product team. In the meantime, most of the remediation can run from the agent: through the MCP it pulls the repo's findings, fixes them in the IDE and updates their status, so the interface is only there to check the result.