
Autonomous access control security for Vibe-coded apps. Our platform finds and fixes live vulnerabilities in your vibe-apps built on Replit, Lovable, Claude Code, Cursor, and other AI-coding tools. 1-prompt makes your app production-ready in minutes without requiring security expertise.




Free
Launch Team / Built With


Render: Get up to $100K in startup creditsCloud infrastructure for founders who want to move fast and NOT break things
Promoted


For apps built on Lovable or Replit specifically, where the developer often doesn't have direct access to the underlying infrastructure or can't freely modify server-side auth logic, how does Perfai actually apply fixes? Those platforms have constraints on what you can change and where, curious whether the "1-prompt fix" works within those constraints or requires exporting the project first.
@ansari_adin
Great question! No export needed. The fixes work within the platform itself.
Perfai doesn't touch your infrastructure. When you say "Fix all Perfai issues" in Lovable or Replit, the platform's own AI agent generates the fixes in your app code, the same code you already own and can edit there. Most access control gaps in vibe-coded apps live in that app layer, like missing auth checks on API routes or client-side-only permission logic, so they're fixable right inside the platform.
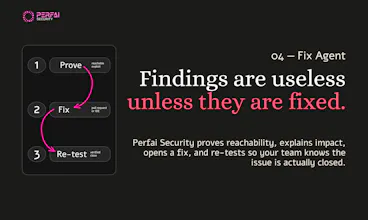
After you review the fixes, say "run security" and Perfai retests your live app to confirm the issues are fixed and nothing is broken. Test, Fix, Retest.
Every finding comes with proof in a pentest-style report. There's a free tier if you want to try it on your own app, and I'm happy to share a 50% discount code plus extra credits. Ping me if you need help onboarding!
Hi @thys_beesman , thanks for asking. Perfai Security offers both, and this is where Perfai Security really shines. We don't just stop at a list of vulnerabilities.
We ship an MCP server (perfai-mcp-server) you drop into your IDE (Cursor, VS Code, or any MCP-compatible agent). Once connected, it pulls your reported issues directly into the editor, and for any issue it generates a context-rich fix prompt with exact endpoint, vulnerability, remediation contexts. Your IDE's coding agent then implements the fix right in your codebase, following your existing patterns and architecture.
We deliberately keep the developer in the loop rather than auto-patching your repo. This way, we never require any code-access. And so the fix lands in your editor where you review and merge it like any other change.
So it's detection → guided remediation → fix, without Perfai Security ever writing to your code behind your back.
TL;DR — Perfai Security maps your app, detects vulnerabilities, provides the fixes, and then retests to verify the issues are patched.
@thys_beesman
Great question! Both. We detect and fix.
Every finding comes with an instant fix you can apply with one prompt in your code agent, like "Fix All", "Fix Critical", or "Fix #2". You don't need to be a security expert or spend hours figuring out how to patch each issue yourself. The Fix Agent hands you exactly what to do.
That's the full loop: our agents test your live app across UI, API, data, and roles, find the gaps, and give you one-prompt fixes. And with drift detection, we catch new issues as your app changes, so you're never relying on a stale report.
All this without paying thousands for a pentest. You get a full pentest-style report on the free tier at perfai.ai. We're also giving away 50% discount codes for the launch. Need extra credits or help onboarding your app? Just reach out. Happy to help!
Congratulations! Does this work with any deployed web app, or is it mainly built for apps created with AI coding tools?
@henry_habib It works with any deployed web app that has a URL. We test black-box from the outside, so we're fully stack-agnostic. It doesn't care whether you hand-wrote it, vibe-coded it, or inherited it. The "vibe-coded" framing is where our solution is needed most right now, but the engine tests any app with roles, APIs, and a database. The only place the AI-coding tool matters is the fix handoff... our Fix Agent delivers remediation through an MCP server you drop into any IDE (Cursor, VS Code, Claude Code…), and it works even if you just want the exact patch to apply yourself. Point it at any URL and see. You can sign up for free or get 50% off our pro plan using the discount code (in pinned comment).
@henry_habib
Thank you!
It works with any deployed web app. If it runs in a browser and has a URL, we can test it. Doesn't matter if it was built by AI agents, a dev team, or ten years ago by a contractor nobody remembers.
We talk a lot about vibe-coded apps because they're the most at risk: shipped fast, often with no security review, and full of access control gaps. But the testing itself doesn't care who wrote the code. Our agents test the running app across UI, API, data, and roles, so any stack works: React, Rails, PHP, whatever.
Same simple flow for everyone: paste your URL, our agents explore, sign up their own test accounts, and get to work. Drift detection keeps coverage fresh as the app changes.
Try it free at perfai.ai and get a full pentest-style report. We're giving away 50% discount codes for the launch too. Need extra credits or help onboarding your app? Just reach out. Happy to help!
Great concept. My team runs into this problem consistently. Even with AI guardrails and instructions, we have to spend valuable hours testing for vulnerabilities.
@zohaib_akmal
Thank you! Your team's experience is exactly why we built this. AI guardrails help, but they can't replace real testing, and doing it by hand eats hours.
Perfai Security does that testing for you. Just enter your app URL. Our agents sign up their own test accounts, then test thousands of permission combos across roles and actions. You get a pentest-style report with proof for every issue. We also run drift detection, so new gaps get caught as your app changes.
Try it free at perfai.ai. Use code PHLAUNCH50 for 50% off any paid plan. If your team wants extra credits or onboarding help, just message me!
Congratulations to the whole @Perfai Security team!! In the AI era, auth and access control issues have become an epidemic, and they're often some of the hardest vulnerabilities to catch before they reach production.
We're actually using Perfai ourselves to help ensure the Dashboard for @Wristband's multi-tenant auth platform is configured correctly and that tenant isolation and authorization rules behave as expected. It's been a great addition to our development process, and seeing it in action has given me an even greater appreciation for what the team is building.
Having personally watched the evolution of this platform, I'm especially excited to see this launch. Huge congratulations to @intesar_mohammed1 and the entire team. Beyond building a great product, they're genuinely friendly people and a pleasure to work with. Looking forward to seeing where Perfai goes from here! 🚀
@jim_verducci
Thank you so much! This comment made our day.
Wristband is exactly the kind of use case we love: a multi-tenant auth platform where tenant isolation has to be right, every time. Watching your team use Perfai to prove authorization rules behave as expected, across every update, is the product working exactly as we dreamed. Auth platforms hold everyone else's front door keys, so the bar is highest there.
And the kind words about the team mean just as much as the product praise. Working with you all has been a pleasure for us too.
For anyone reading: this is what Perfai does. Test your live app's access control across UI, API, data, and roles, with drift detection catching gaps as you ship. Try it free at perfai.ai and get a full pentest-style report. We're giving away 50% discount codes for the launch. Share your app URL and I'll get you a free report personally. Need extra credits or onboarding help? Just reach out!
Perfai reduces the barrier to security testing as the workflow is as easy as pasting the URL. Congrats on launching today.
Much appreciated @himani_sah1
That’s exactly what we’re trying to solve. With so many vibe-coded apps going live, security testing needs to fit the builder’s workflow. Perfai Security makes it possible for solo founders and small teams to deep-test access controls in live apps without needing enterprise security teams, long setup cycles, or manual testing expertise.
@himani_sah1
Thank you! That's exactly the goal.
Security testing has always had a high barrier: expensive pentests, complex tools, or needing an expert on the team. Most builders just skip it. So we made the barrier one paste. Drop in your URL, and our agents explore your app, sign up their own test accounts, and test everything across UI, API, data, and roles.
No setup project, no security background needed. And with drift detection, coverage stays fresh as your app changes, so it's not a one-time check.
Try it free at perfai.ai and get a full pentest-style report. We're giving away 50% discount codes for the launch too. Need extra credits or help onboarding your app? Just reach out. Happy to help!
Congrats on the launch, team!
AI-coding tools let us build at lightning speed, but security usually gets left in the dust. Perfai fixing live vulnerabilities in vibe-coded apps with a single prompt is brilliant.
This bridges the gap between shipping fast and staying secure. Absolutely crushing it. Wishing you a huge success!
@dr_mohammed_nadeem
Thank you so much! You nailed it. Vibe coding is fast, but security can't keep up. That's exactly why we built Perfai.
Just enter your app URL and our agents test it like a real pentester would. You get a pentest-style report with proof for every finding. We also do drift detection, so every new release gets tested for new gaps.