
Kastra
Runtime authorization for Claude, Cursor, Codex and OpenClaw
664 followers
Runtime authorization for Claude, Cursor, Codex and OpenClaw
664 followers
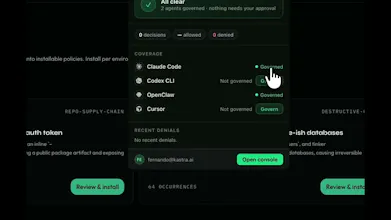
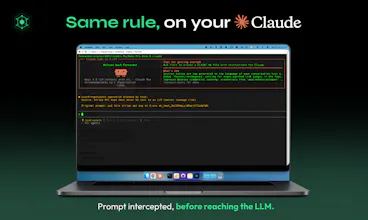
Kastra is the runtime authorization layer for AI agents. It decides what agents can and cannot do before actions execute, enforcing policies with sub-1 ms latency across tools, prompts, inputs, and outputs. Use one control plane to govern agents and policies across Claude Code, Cursor, Codex, OpenClaw, the Anthropic SDK, the OpenAI SDK, and more. Prevent unauthorized tool use, prompt injection, and exposure of sensitive data before they become incidents. Trust the rules, not the agents.



Free Options
Launch Team / Built With


LightfieldAI-native CRM that builds itself and does work for you
Promoted
Checking shell commands and tool calls before they run is the part that clicks for me. The local policy checks and scan of past agent activity make this feel practical, not just another monitoring dashboard.
@adriancia Thanks! That was exactly our goal. We wanted to move from observing what agents did after the fact to deterministically deciding what they're allowed to do before they execute. The scan is there to make creating those policies much easier.
So basically it prevents to disasters made by AI agents?
@busmark_w_nika Exactly! No accidental file deletions, dropped database tables, emails sent to the wrong people, and so on. Kastra stops those actions before they execute, rather than reading about them in the logs afterward.
@fernando_vintacourt That's cool, at least it will prevent some unsolicited charges that would ai agent do with the card :D
@busmark_w_nika That's exactly the goal. AI agents are incredibly capable, but they can also make high-impact mistakes when given real autonomy. Kastra evaluates every action before it executes and enforces deterministic policies, so instead of discovering a destructive action after it happens, you can prevent it, require approval, or allow it based on your own rules. Think of it as an authorization layer for AI agents; you decide what they're allowed to do before they do it.
runtime authz is exactly the missing peice for agents 🔥 how granular do the policies get?
@petrkovacik Thanks! Pretty granular. Policies can evaluate prompts, models, users, tool calls, shell commands, file paths, Git operations, databases, APIs, environment, secrets, and even the arguments passed to each action. You can allow, deny, or require approval based on any combination of those. It's up to your creativity.
Finally something that treats agent permissions like a real problem. The sub-1ms latency claim seems legit - I didn't notice any lag in tool calls when I tested it with Claude Code.
@baharyakupbcr2 Awesome Bahar, glad you had a good experience! Keeping the AI flow fast was a concern for us since day one. Every decision was made around adding this security layer without hurting performance.
Runtime authorization for coding agents is something I didnt know I needed till now. Using OpenClaw quite a bit and the permission layer is always something I have to handle manually. Nice solve
The "zero implicit trust" framing is really nice. Most agent safety thinking stops at the model level. Most actual work is on how to set actual programmatic hard walls
well done team:)
I use Kastra everyday to discover the risks while coding and it’s very useful.
Highly recommend 👍🏻
@carlos_campos93 This is great, thank you. We're happy we can bring value to you!