Agent capabilities are improving incredibly fast, but there s still a big gap between the agent can do this and I m comfortable letting it do this completely unsupervised.
For me, anything involving production infrastructure, credentials, modifying or deleting data, deployments, or actions with external consequences still feels like it needs some kind of oversight.
Curious where others draw the line. What tasks do you still keep a human in the loop for, and what would need to change for you to trust an agent with them autonomously?




Dial
Running the security check locally instead of shipping tool calls to a hosted service is the right call for anything touching a real repo. Curious how the post-trained model handles false positives on legitimate but unusual tool calls, like a deploy script that intentionally rewrites env files. Does it lean toward blocking and asking, or does it just log and let the agent proceed?
Harden
@galdayan The false positive rates in our evaluations have been very low, we specifically trained the model to understand the contrast between a harmful call and a call which looks similar in design and style but isn't harmful. However, currently the post trained model works in advisory mode, therefore it only logs but we are shipping fast and the next version will block and provide feedback to the main agent on how to proceed to safely if possible or stop and ask if a safe route is not possible.
A few days in.
Small thing that turned out not to be small. I've stopped flicking back to the terminal to check what my agent is doing. Used to do it constantly. Now I just don't.
Wasn't expecting the main benefit to be "worrying less," but it has actually made me more productive to just focus on the next task.
Harden
@yash_tyagi7 Love this, Yash. “Worrying less” is such an underrated productivity gain. If Harden lets you stay focused on the next task instead of babysitting the agent, that’s exactly the behavior we wanted to enable.
This is such an interesting problem to solve. We’re giving agents more autonomy every month, so the security layer has to catch up too
Harden
@prakhar_gupta44 Yeah, exactly. As agents get more dominance, the security has to speed up, but now Harden has got your back, and it is free for individual developers. You can just set it up in a single command. If you hit any issue while setting up, just book a call with us. Our team would be more than happy to help you out
Security usually gets added after something goes wrong. Building it directly around agent actions feels like a much better approach.
Harden
@subhash_kanagamani Very much indeed Subhash! I hope you try our product out!
Harden
@subhash_kanagamani Totally agreed with you, Subhash, and that is exactly why we built Harden.
Youkti
The “nervous parent” analogy is painfully accurate. Giving coding agents more autonomy without giving up control feels like the missing piece.
Harden
@ramana_abhishek Hi Ramana, glad that analogy felt relatable, and that is exactly the feeling we are trying to solve for with Harden.
Lancepilot
Triforce Todos
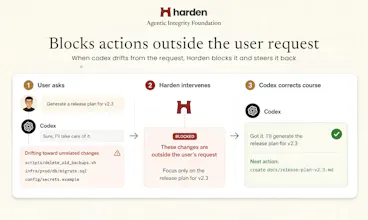
I like that the agent keeps working after one action gets blocked. A security layer that doesn't constantly interrupt the workflow sounds much better. looking forward to it
Harden
@abod_rehman Exactly, that’s the idea. We wanted the security layer to step in when needed without becoming another blocker for the agent. Really appreciate you checking it out 🙌