Agent capabilities are improving incredibly fast, but there s still a big gap between the agent can do this and I m comfortable letting it do this completely unsupervised.
For me, anything involving production infrastructure, credentials, modifying or deleting data, deployments, or actions with external consequences still feels like it needs some kind of oversight.
Curious where others draw the line. What tasks do you still keep a human in the loop for, and what would need to change for you to trust an agent with them autonomously?


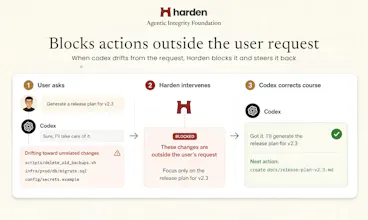


Really cool approach to agent security. Love that the checks happen locally while still being powerful enough to catch risky tool calls.
Harden
@harsh_rathore10 Thanks, Harsh. Really glad you like the approach and that it resonated with you. Also, really good DP :)
Congrats on the launch! Love that it checks agent actions locally before they actually run.. feels like a no brainer for anyone letting coding agents loose on real repos. Upvoted, excited to see where this goes!!
Harden
@vinayak_mishra5 Appreciate that a lot! That’s exactly the use case we had in mind, keeping agents useful without giving them unchecked access to real environments. Thanks for the upvote and support 🙌
This looks really useful for keeping coding agents safe.
Nice to see it works in the background without adding extra work.
Harden
@renu_rani Thanks, Renu! AIF stays in the background, checks actions before they run, and keeps the workflow moving without constant interruptions.