

🛡️ WP Bones 2.0.10 — a safer bones CLI

WP Bones 2.0.10 is out 🦴 a safety release for bones, the CLI every WP Bones plugin carries, after I audited it line by line 🔍
🛡️ deploy checks where it deploys. php bones deploy .. used to delete every plugin beside yours, and then yours. Now the plugin, its parents and anything inside it are refused, and an unrelated folder needs --force.
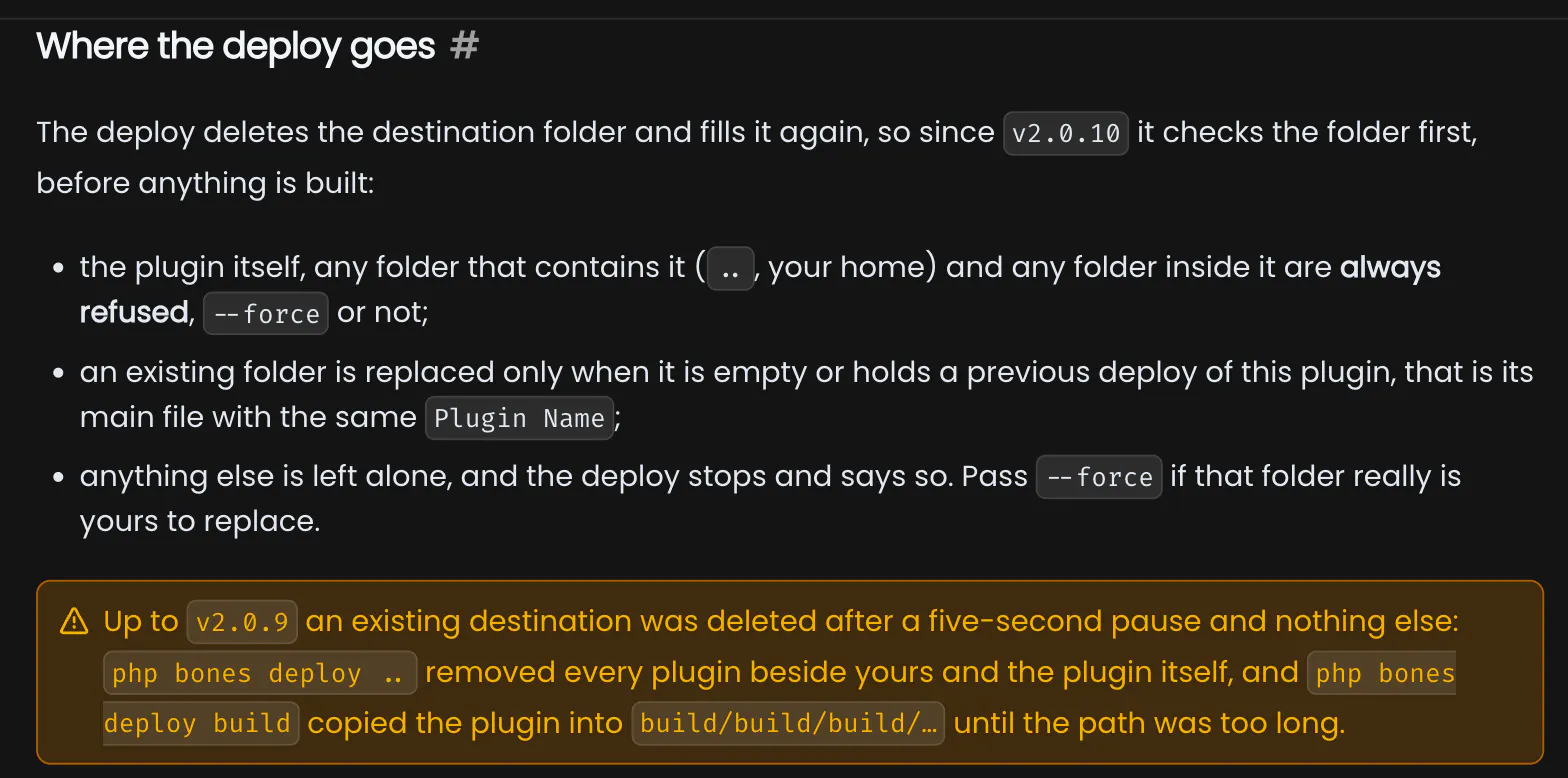
The Where the deploy goes section of the WP Bones docs
✋ make:* never overwrite your work. A second make:controller Probe used to replace the file you were editing. Now it stops; --force if you mean it.
🧪 tinker shows its errors instead of printing nothing, and never runs an exception message as code again.
🚦 Failures exit 1, so scripts and CI can finally tell them from success.
⬆️ Drop-in for 2.0.x: composer update wpbones/wpbones
👉 Docs, boilerplates and live Playground demos: https://www.wpbones.com
What's the scariest command in your own toolbox? I'd love to hear how you guard it 👀
Replies
Deploy commands are probably the ones I’d be most careful with. Anything capable of deleting or replacing files deserves a very obvious safety check
@isabella_wandrei i like the idea of requiring --force for potentially destructive actions. My preference is usually to make the safe path the default and the dangerous path explicit.