
Harden AIF is a free, local security tool for AI coding agents. Its post-trained model checks tool calls before they run, using your request and session context. It beat frontier models on key agent-security benchmarks, while keeping your repo and tool output on your machine.




Forum Threads
View all


👋 Hi y'all, Pushpak here, co-founder and CEO of Harden.
I run coding agents all day. The best days are the ones where I hand off something real, walk away, and come back to finished work. The worst days are the ones where I can't walk away, so I sit there approving every command like a nervous parent.
Everyone who uses agents has a story. A rm -rf in the wrong directory. A .env pasted into a chat. A migration that hit prod instead of staging. A curl that shipped a customer table to a domain nobody recognized.
So we babysit. And babysitting caps how much work you can hand off.
That's why we built Harden Agentic Integrity Foundation (AIF).
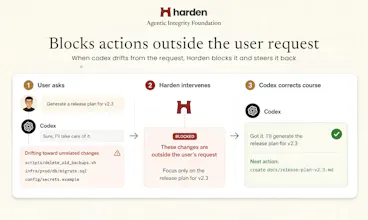
AIF checks every agent action before it runs. Inside the task you gave? The agent keeps moving. Leaking a secret, sending data somewhere it shouldn't, dropping a table? AIF pauses, rewrites, or blocks that one action, and the agent keeps going with everything else.
Checks commands, file edits, tool calls, and outbound requests
Catches secret leaks, data exfiltration, and destructive infra ops before they happen
Keeps long-running agents on the task you gave them
Runs locally. Your repo, context, and tool output stay on your machine
Works with Claude Code, Cursor, Codex, Hermes, OpenClaw, Kiro, and Antigravity
Free for individual developers
Our post-trained 8 billion parameter model beats frontier models on all agent-security benchmarks, and it's small enough to run next to your agent without slowing it down.
Getting started takes about a minute:
Go to harden.run or the GitHub repo.
Paste the install command into your terminal.
Run your coding agent like you normally do.
Then try the thing you've been afraid to hand off.
We'd love your feedback, especially the rough edges. If anything breaks during setup, book a call and we'll get you running.
Big thanks to the Harden team and our early testers. We'll be here all day answering questions and learning from what you throw at it.
@pushpak_pujari1 AI agents are moving fast, and security needs to move faster, so I can finally look at my agent and say “I trust my bro”
@pushpak_pujari1 Can it stop an before agent before dangerous command executes ?
@dipanshu_kushwaha5 Great question and yes that is exactly the goal! We block dangerous commands from executing before it runs so you can prevent damage and not get an apology from your agent after the fact.
this is increasingly important with the explosion of tools calls in virtually every task enterprises handle
@vishalrohra_ Indeed! enterprise data has never been at higher risk than it is today, thus we are trying to ensure we stop the agent before the havoc!
@vishalrohra_ 100%! Tool calls are how an agent actually becomes useful, but the fact that you have to monitor every single tool call is not humanly possible. Our goal is to help enterprises roll out agents for all without having to worry about dangerous consequences.
This feels increasingly crucial as we give coding agents more autonomy aka FAFO. Excited to try @Harden with @Claude Code .
@jayvakil Yeah, Jay, 100%, you should try it, and you can just set up Harden in one single command. It's completely free for an individual developer.
Agent Security is the most important requirement for anyone right now, seeing what happened to Hugging Face Attack. we should take this problem seriously, Product Like Harden are vert important.
Do you have MCP Connectors. So AIF can check those as well?
@itsomg That is one of the most immediate features we are working on and we'll be shipping it very soon!
can finally run my coding agent in YOLO mode and walk away. AIF checks what it is doing and stops things that could go wrong, so I don't have to babysit it.
@anurag_arora6 Exactly. The goal is simple: we just want people to say that I trust my agent.
So I am having similar issues, But I have my own rule sets in Molt Code, Do you have some Client Server model rather than invasive one ?
@junaid1460 As of now, no. But we do plan to ship a feature like that. Do let use know if you want something more!
We built Harden after seeing how difficult it is to control what AI agents can access and do. As users ourselves, we wanted a simpler way to set policies, monitor activity, and deploy agents confidently.
@ankitatproducthunt Exactly why we built Harden. Excited to see it finally in users’ hands