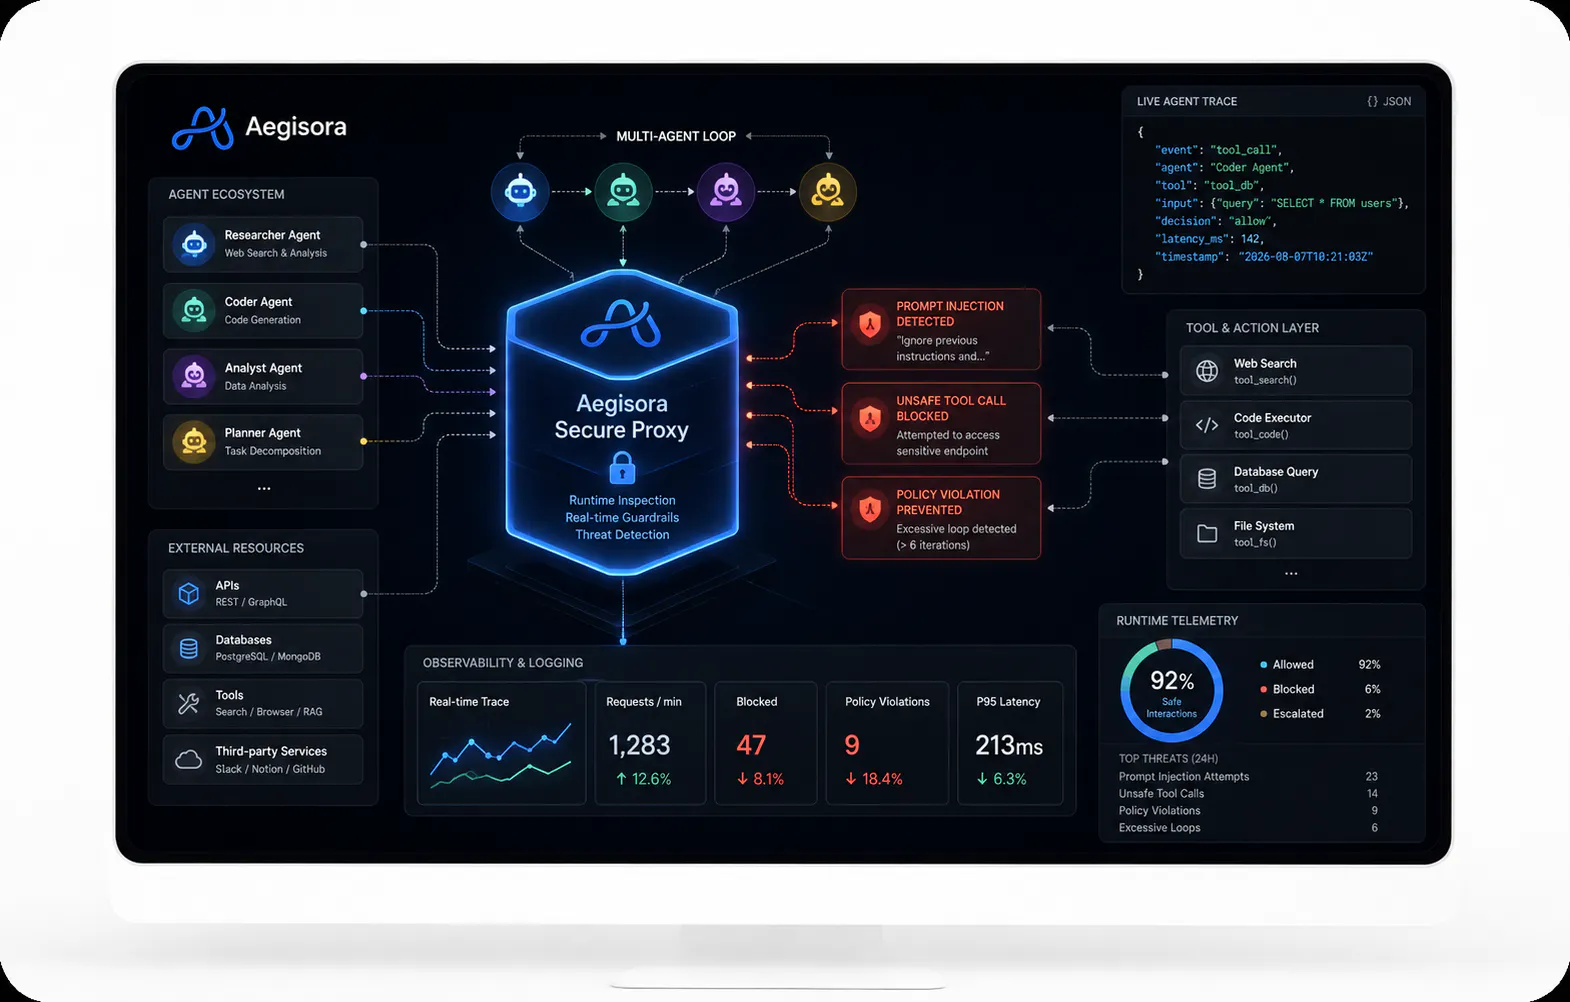
We ve all seen the dazzling demos of multi-agent systems executing complex workflows. But as developers start deploying these agents into deep production with direct API access, a terrifying reality sets in: debugging non-deterministic behavior.
When an agent hallucinates a tool call parameter, enters an infinite reasoning loop, or gets subtly manipulated by an indirect prompt injection, tracing why it happened at runtime is a nightmare. Traditional logs just show a wall of async LLM requests.
While building Aegisora, we realized that observability and security for agents can't be treated like traditional web apps you need real-time runtime inspection and deterministic guardrails.
I m curious to hear from builders here: What is your current strategy for monitoring and debugging autonomous agents when they misbehave in production? How do you catch runtime anomalies before they hit your external APIs?
As we move rapidly from experimental chat interfaces to fully autonomous agents with direct API access, runtime security is becoming a massive blind spot.
While building Aegisora (our open-source, zero-latency runtime proxy), I constantly hear terrifying stories from engineering teams about agents trying to execute unauthorized API calls, looping endlessly, or silently leaking PII because static guardrails and prompts failed.
We are officially open-sourcing the Aegisora core engine! Stop breaking AI workflows with rigid firewalls. Aegisora acts as an escalation boundary, pausing risky LLM tool calls for human review with zero latency. Built for enterprise AppSec and Agentic AI builders.
Stop selling abstract "AI safety". Enterprises buy operational control. Aegisora is an open-source, zero-latency proxy layer built for AppSec teams. Intercept malicious LLM actions, enforce least-privilege API access, mask PII on the fly, and generate readable audit logs for autonomous agents—without the bloated middleware.