
InsurStaq
Private AI security engineer for your Mac
3 followers
Private AI security engineer for your Mac
3 followers
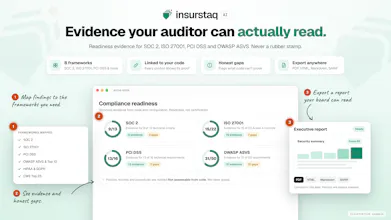
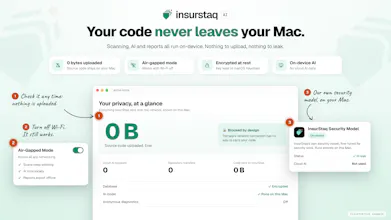
InsurStaq is a private AI security engineer for your Mac. Point it at a repo: it maps routes and auth, finds injection, exposed secrets (Git history too), vulnerable dependencies and IaC risks, and traces attack paths from the internet to the exact line. InsurStaq's own security model, fine-tuned for security work, explains findings and drafts fixes you approve, each re-scanned on your Mac. Readiness evidence for SOC 2, ISO 27001, PCI DSS and OWASP ASVS. Source code is never uploaded to us.


Payment Required
Launch Team / Built With


AWS Activate CreditsCredits that fuel your startup’s next milestone
Promoted
Hi Product Hunt — I built InsurStaq because the security tooling market assumes you can hand your source code to someone else’s server, and a lot of teams simply cannot.
The design decision that shapes everything: the AI does not find the issues itself: deterministic scanners and the taint graph produce candidates first, and the model reasons over that evidence packet (finding, file, line, path); its output is schema-validated. That keeps it grounded, and it keeps the model small enough to run on a laptop.
Three things I’d rather say upfront than have you find later:
– It is not a penetration test, and it does not certify anything.
– It is macOS on Apple silicon only today.
– You download it from your account and activate each Mac by signing in; after that it works offline.
Happy to answer anything about the architecture — the read-only Git engine that never runs hooks or filters, the SBPL sandbox for untrusted tooling, or why the compliance output is deliberately hedged. Ask away.