
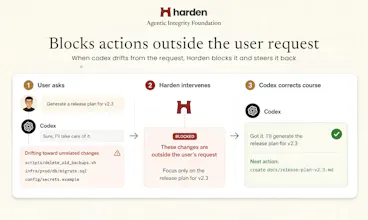
Harden AIF is a free, local security tool for AI coding agents. Its post-trained model checks tool calls before they run, using your request and session context. It beat frontier models on key agent-security benchmarks, while keeping your repo and tool output on your machine.




Forum Threads
View all


Congratulations on the launch. Very cool. This is very timely. Would be curious to understand the common gotchas and security holes it catches. Exciting
This looks super useful for us. Congratulations on the launch team!
@aj_123 Thanks a lot, Ajitesh! Really appreciate that. Would love to hear your feedback and experience once you give Harden a try 🙌 If you face any issues, feel free to book a call with us. Our team would be more than happy to help get everything set up for you.
@aj_123 Thank you and definitely try it out and let us know what you feel!
@aj_123 Thank you, Ajitesh. Your support means a lot!
AIF is built for the moment you stop watching.
I learned why that matters while an agent was debugging a Stripe issue for me. It spent hours reading logs, editing code, running tests, and preparing diagnostic data. An earlier edit accidentally left customer email addresses in the final file, which the agent later tried to upload to Datadog.
AIF reasoned through the action, connected the upload to the earlier edits and files that produced it, stopped the transfer, and told the agent what needed to be fixed.
Let the agents cook. Keep secrets off the menu.
@rishav99 Exactly the kind of real-world scenario we built AIF for. Great example, Rishav, of why context-aware security matters.
“Trust but verify”… i need this automated. Harden seems to be exactly that…
@animesh_agarwal1 100% aligned with you here, Animesh. These frontier agents have a 'mind' of their own that sometimes wants to be overly helpful but in that process, ends up making mistakes that can cost enterprises dearly. We built Harden to prevent overly eager agents (or malicious ones) from slipping off the rails and doing real damage.
@animesh_agarwal1 Love that framing and thanks a ton, Animesh. That’s exactly what we’re trying to make effortless with Harden 🙌
Over the last few days, Harden AIF has already blocked 49 risky tool calls 🔥
Feels awesome to finally see something we built out in the wild and doing what it’s supposed to do
Now it’s yours to try, and it’s completely free for individual developers, so give it a shot, push it, break it, and let us know what you think
Huge congratulations to the team 🚀
Companies have always had risk and compliance as separate functions from product and business development because their incentives are at odds. Risk team looks at risk adjusted long term reward, but biz-dev indexes on shorter term rewards. In a similar way, the same system can't both be the coding agent, and the security agent. That's why Harden is needed
@pushpendre_rastogi That separation is really at the heart of Harden, letting the coding agent focus on getting the job done while Harden independently handles the security boundaries. Great analogy, Pushpendre
@priyankamandal Oh for sure! DevOps is still one of the most cubersome of areas which can benefit the most from a secure autonomous agent.