

I’m building Permetra an open-source access graph for Supabase
Hey everyone 👋
I’m building Permetra, an open-source security tool for Supabase.
The idea is simple:
Who can access what in your Supabase application and why?
As an app grows, access control gets distributed across users, roles, tenants, database grants, tables, functions, and RLS policies. It can become difficult to understand the complete access picture.
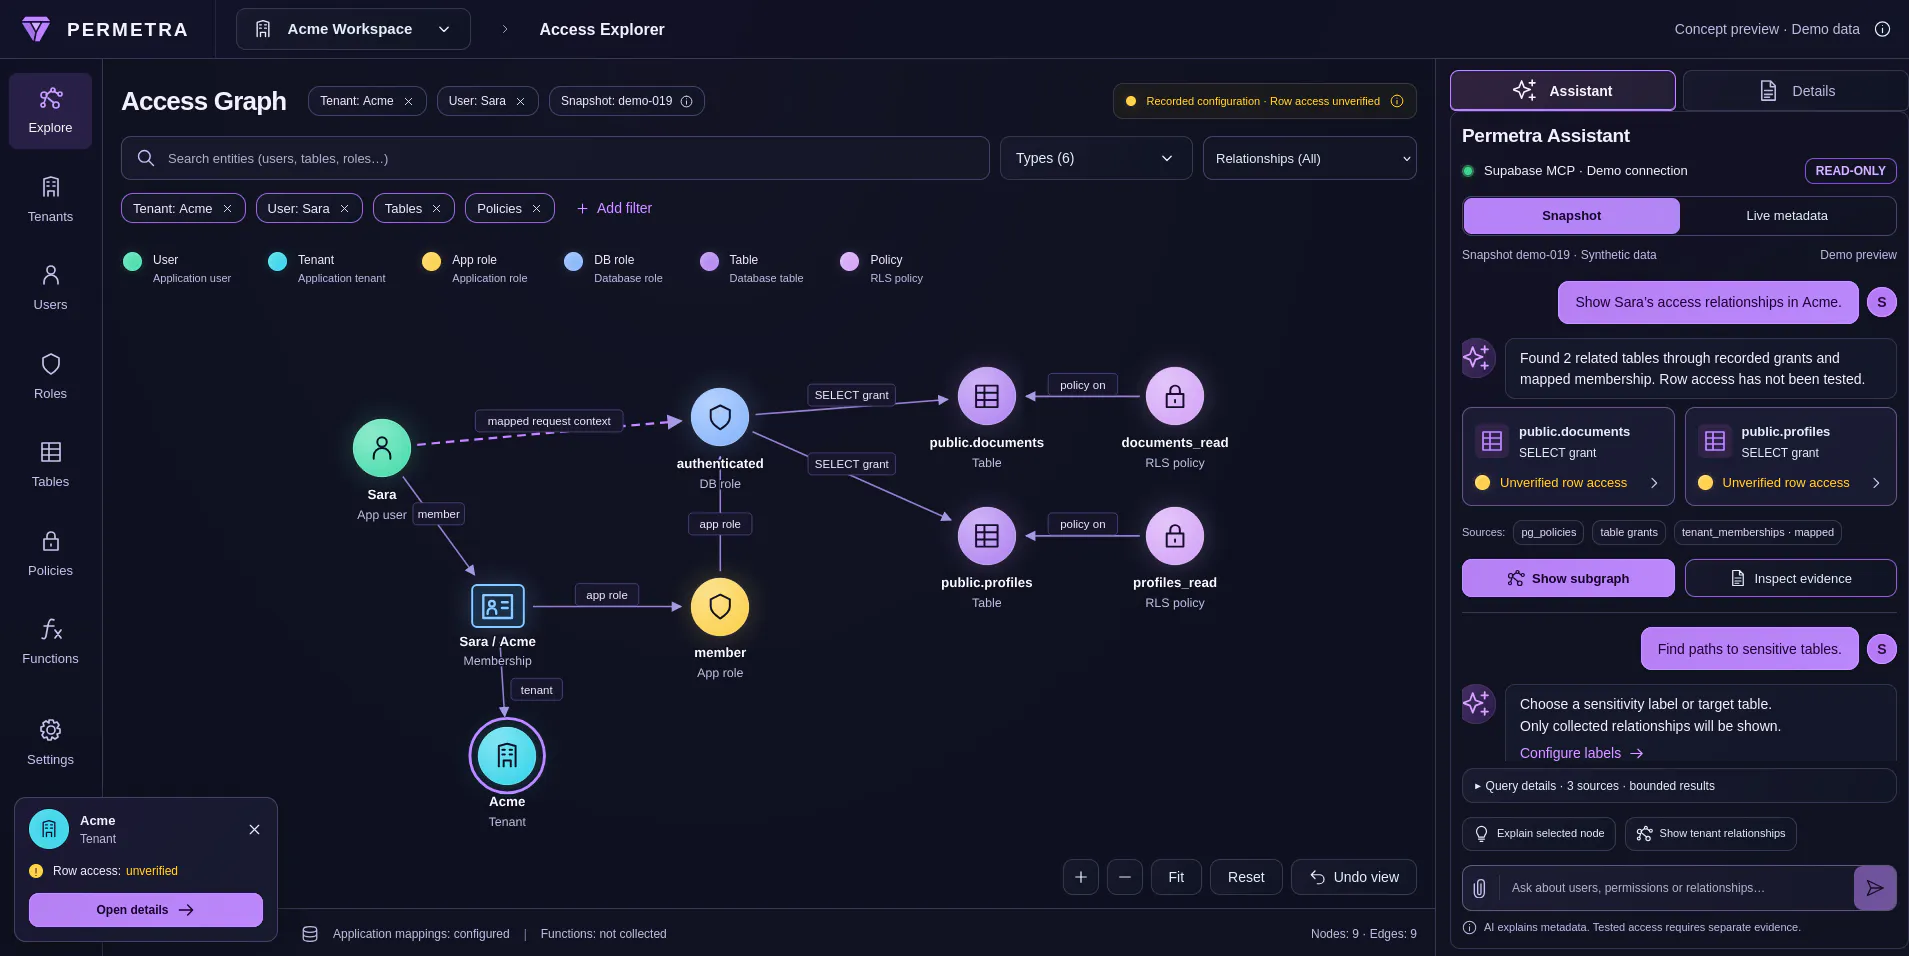
Permetra turns this into an interactive, BloodHound-inspired graph so you can explore relationships and access paths visually.
The goal is to help developers:
Visualize users, roles, tenants, tables, policies, and permissions
Understand why a user can access a resource
Discover unexpected access paths
Review tenant isolation and authorization
Make Supabase security easier to understand
I’m still building the first version and would love feedback from Supabase developers, security engineers, and open-source contributors.
If you use Supabase: Would something like this be useful for you? What would you want it to detect first?
Early testers and contributors are very welcome 🚀
Replies