Launched this week

TryTrustable
Compliance, security and AI governance on one control graph.
2 followers
Compliance, security and AI governance on one control graph.
2 followers
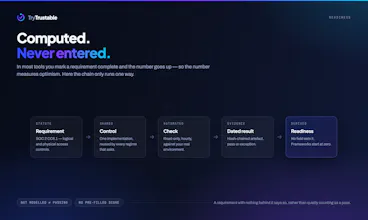
One control, many regimes: logical access answers SOC 2 CC6.1, ISO 27001 A.8.2, GDPR Art. 32 and DPDP s.8(5) from a single result. Evidence is hash-chained as controls run — no screenshots, and exceptions are recorded as carefully as passes. Unusual: security testing (SAST, SCA, DAST, IaC, secrets) runs in your own CI rather than inferred from questionnaires. Consent sits on the same graph with a proof-of-consent ledger. Readiness is computed, never entered. Frameworks start at zero.