Launching today

landmine
Lockfile in. Known bugs out. Before your agent edits.
7 followers
Lockfile in. Known bugs out. Before your agent edits.
7 followers
Your agent never checks GitHub for bugs in your exact versions. landmine does: it reads your lockfile, finds open issues filed against those versions, and gives the agent the bug and the workaround via AGENTS.md, a pre-edit hook or MCP. Free and open source.



Free
Launch Team / Built With


AWS Activate CreditsCredits that fuel your startup’s next milestone
Promoted
Hey Product Hunt 👋 I'm Devansh, I built landmine.
It started with my coding agent writing code that matched the docs but broke on the version I actually had installed. Every time, the bug was already on GitHub, filed against that exact version, often with a workaround in the comments. The agent just never looked.
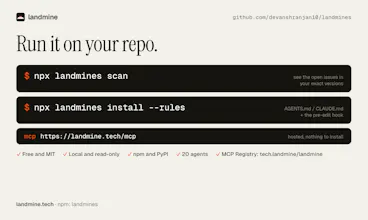
landmine reads your lockfile, finds the open GitHub issues filed against the exact npm and PyPI versions you pin, and puts them where your agent will see them: a short known-bugs section in AGENTS.md / CLAUDE.md, a pre-edit hook for 20 agents, and an MCP server.
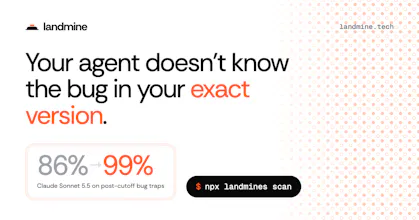
I wanted proof it helps, so I built a benchmark from bugs filed after the model's training cutoff. Claude Sonnet 5.5 went from 86% to 99% with landmine. The surprise: when I gave it web search or the Context7 docs MCP instead, it never used them once in 84 sessions.
Honest caveats: it's my own benchmark, only Claude Code was tested, and about 3 in 4 results are confirmed real when checked by hand.
Try it with no install:
→ type any package at landmine.tech
→ or add the hosted MCP: https://landmine.tech/mcp
→ or in a repo: npx landmines scan
It's free and MIT. What does it find in your lockfile? I'd especially love to hear about the false positives.
Is this meant for autonomous code review by agents or for documentation?