iDefender - Behavior-Driven Intelligent Defender, combines HIPS granular control with EDR-grade attack chain analysis — monitoring what programs actually do, not what they look like. Every file operation, process action, and network connection is evaluated in real time, so known malware, unknown variants, and zero-day attacks are all caught the moment they act.
I'm aliangbo, founder of iDefender. Excited (and a bit nervous) to launch here today.
Here's the problem we kept running into: traditional security tools mostly judge programs by what they look like — signatures, hashes, reputation. But modern attacks don't play by those rules. A zero-day has no signature. A new malware variant has no known hash. By the time it's identified, it's already done damage. So we built iDefender around a different question: what is this program actually doing, right now? iDefender combines HIPS-level granular control with EDR-grade attack chain analysis. Every file operation, process action, and network connection is evaluated in real time — so known malware, unknown variants, and zero-day attacks are all caught the moment they act, not after. A few things that make it different: • Behavior-first, not signature-first — no waiting for threat intel updates • Granular control — you decide what gets allowed, blocked, or flagged • Attack chain visibility — see the full story, not just a single alert • Real-time evaluation — file, process, and network activity, all monitored We'd love your feedback — especially from security folks, sysadmins, and anyone who's tired of alert fatigue. A couple of questions for you: What's the biggest gap you see in current endpoint security tools? Would you rather have more control (and more decisions to make) or more automation? Drop your thoughts below — I'll be here all day answering questions. 🙏




I'm aliangbo, founder of iDefender. Excited (and a bit nervous) to launch here today.
Here's the problem we kept running into: traditional security tools mostly judge programs by what they look like — signatures, hashes, reputation. But modern attacks don't play by those rules. A zero-day has no signature. A new malware variant has no known hash. By the time it's identified, it's already done damage.
So we built iDefender around a different question: what is this program actually doing, right now?
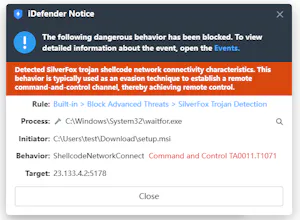
iDefender combines HIPS-level granular control with EDR-grade attack chain analysis. Every file operation, process action, and network connection is evaluated in real time — so known malware, unknown variants, and zero-day attacks are all caught the moment they act, not after.
A few things that make it different:
• Behavior-first, not signature-first — no waiting for threat intel updates
• Granular control — you decide what gets allowed, blocked, or flagged
• Attack chain visibility — see the full story, not just a single alert
• Real-time evaluation — file, process, and network activity, all monitored
We'd love your feedback — especially from security folks, sysadmins, and anyone who's tired of alert fatigue.
A couple of questions for you:
What's the biggest gap you see in current endpoint security tools?
Would you rather have more control (and more decisions to make) or more automation?
Drop your thoughts below — I'll be here all day answering questions. 🙏