Launching today

Amber
Permission-aware RAG for enterprise, built on Google Drive
2 followers
Permission-aware RAG for enterprise, built on Google Drive
2 followers
Amber is open-source RAG for enterprises. It inherits permissions from Google Drive, enforces them inside every search query, cites every answer, and keeps an append-only audit log, so teams can roll out AI search without leaking documents.




Free
Launch Team

CloudflareDeploy serverless functions globally in seconds
Promoted
Hey Product Hunt 👋 I’m Anushka, founder of Kathalyst. Justin and I built Amber because the hardest part of enterprise RAG isn’t the retrieval. It’s the permissions.
The problem: most AI search tools index everything and rely on the prompt to behave. One wrong query, and an intern gets answers drawn from salary sheets, or a contractor from M&A docs. That risk is why many security teams block AI search rollouts.
Amber’s approach: don’t build a second permission system, inherit the one you already trust.
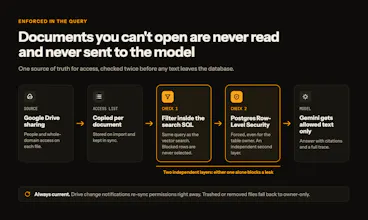
Drive is the source of truth. Amber reads each file’s sharing settings and stores them as its access list.
Enforced in the query, not after it. Access is checked in the same SQL as the vector search, so a document you can’t open is never read, never sent to the model, and never quoted. Postgres Row-Level Security (forced, even for the table owner) is an independent second check.
Always current. Permission changes arrive through Drive notifications, and edited files re-index after 5 quiet minutes.
Traceable and auditable. Every answer has citations plus a trace of the rewrite, retrieved passages, scores, and what was cited. Admin actions, sharing changes, and searches go to an append-only audit log.
Security by default. Server-side Google sign-in with PKCE, HttpOnly session cookies, CSRF protection, KMS-encrypted refresh tokens, least-privilege Drive scope, and roles that live in Postgres, not tokens.
Agents on a leash. The agent can propose edits to Docs and Sheets, but a human must approve every change.
Stack: Gemini (paid tier), pgvector + Postgres full-text hybrid search, FastAPI, Next.js, Firebase Auth, Cloud Run.
What it doesn’t do yet (honest limits): access is mapped for individual users and whole domains. Google Groups and shared drives aren’t mapped, so Amber under-shares rather than over-shares. Uploads are capped at 30 MB. I’m not claiming any compliance certification.
I’d love input from people who’ve tried to roll out AI search at work:
What would your security review ask for first?
Which sources beyond Drive would you need (SharePoint, Confluence, Slack)?
Ask me anything about the ACL design, the RLS setup, or the sync model.