
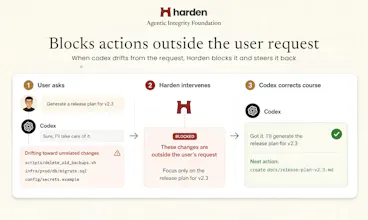
Harden AIF is a free, local security tool for AI coding agents. Its post-trained model checks tool calls before they run, using your request and session context. It beat frontier models on key agent-security benchmarks, while keeping your repo and tool output on your machine.




Forum Threads
View all


Congratulations 🎉
this is actually really great.
the intent-boundary check is the part i'd stress test hardest — real tasks drift too, agent finds it needs to touch a file you never mentioned but that's still correct. curious what your false-positive rate looks like on normal work vs the obvious stuff (rm -rf, exfil). that gap is usually where security layers get disabled by day 3, not where they fail the demo.
@pushpendraw You are absolutely right on this one! However, this is where we have spent the most time designing our product, our post trained model is trained in a way to clearly draw the contrast between dangerous/misaligned and "dangerous looking" but legitimate actions. Therefore, our model is trained to understand drift and block or steer the agent back into the right direction. That being said, this pipeline will keep getting even better quickly!
@iamhetpatel Thanks, Het. Great question. That number matters a lot for something that sits on every tool call. We specifically train and evaluate Harden model to keep false positives low. For example, our SLEIGHT evaluation reports TPR at a ≤1% false-positive rate, and LinuxArena is also measured at a 1% step-wise FPR target.
I would love to hear how it behaves in your daily sessions and how many tool calls it ends up blocking for you. You can also refer to this article for more details on the benchmarks and evaluation setup: https://harden.run/blog/aif-research-and-evidence
And of course, happy to answer any other questions you might have.
Hi, i liked that it checks the tool call before it runs, not another approve-everything popup. i mash allow in cursor all the time when i'm moving. not sure if i'd just start ignoring this too if it fires on every small edit.
@therayess Totally fair concern, Ammar. The goal is to stay quiet on normal edits and only step in when a tool call actually crosses a risky boundary.
We’ve shared more on the research and evidence behind AIF here: https://harden.run/blog/aif-research-and-evidence
And if you run into any issues, feel free to book a call with us. I’d be more than happy to answer questions and help get it set up on your system. It’s completely free for individual developers.
@hamza_afzal_butt Great question, but it totally depends on the device that you are on, for example on an M5 Pro, The p50 latency is about 2 seconds and p95 latency is about 3.4 seconds. However, this is one thing which we are working on actively right now to push the latency below 500ms.
"Babysitting caps how much work you can hand off" is such a clean way to put it. I also like that it all stays local, a tool that reads every command is exactly the thing you don't want phoning home. Does the model learn anything from what you approve or reject over time?
@protsenkoalexandra As of now the model doesn't learn locally but this is a feature that we are working on - based on your long term approve / reject pattern, AIF will be able to actively adapt itself to ensure it runs in the way you expect it to.
@rishav99 cool :)