
Radar
Open-source Kubernetes UI and MCP server
870 followers
Open-source Kubernetes UI and MCP server
870 followers
Radar is an open-source Kubernetes UI and MCP server. It shows topology, resources, events, Helm, GitOps, live traffic and security checks, and it gives AI agents the same view: click Investigate on any issue and your agent finds the root cause. Run it locally as a single binary or in-cluster with RBAC and OIDC, no account needed. Radar Cloud adds fleets, alerts and hosted investigations.
This is the 2nd launch from Radar. View more

Radar
Launching today
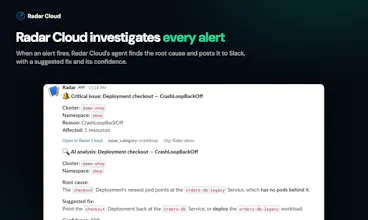
Your agent knows Kubernetes. It doesn't know your cluster. Radar (open-source) gives it context over MCP: ranked issues, a change timeline, logs and owners in one view. New: click Investigate on a failing workload. Claude Code, Codex or Cursor finds the root cause, read-only, with evidence for each claim. In our benchmark of 50 live faults across six tools, Radar found the most root causes. Radar Cloud investigates every alert and posts findings to Slack.




Free Options
Launch Team / Built With


Hey Product Hunt, Nadav here, one of the people behind Radar.
We launched Radar here in May as an open-source Kubernetes UI. Unsurprisingly, more and more people have been telling us since then that they want to point their AI agents at their clusters. Agents have become really smart, but they burn a lot of time and tokens poking around the cluster with kubectl to understand what’s going on and piecing together the puzzle - and even then often miss the change that someone made ten minutes before things broke.
Radar's MCP server gives your agent (Claude Code, Codex, Cursor, Copilot, etc) the cluster already put together: issues detected, a history of events and changes to Kubernetes resources, topology and relationships between objects, logs and metrics.
We benchmarked it - same agent with Radar found root cause 3x (!) faster and 80% cheaper than with plain kubectl.
Click Investigate on any issue and Radar runs your own agent CLI, read-only, on your machine. You get the root cause, the evidence for each claim, and a fix that runs only if you approve it. Radar Cloud does the same when it detects an issue or an alert fires, and posts the answer to Slack.
We also ran six AI SRE tools on 50 live faults. Claude Code on Radar's MCP got 44 right, the most of the six, and was the fastest and cheapest. Method and every run: https://radarhq.io/benchmark/ai-sre-tools
Radar is free and open source, Apache 2.0:
How do you debug your clusters today, and what would you want an agent to take on next?
publishing every run of the 50 fault benchmark, misses included, is waht made me trust the 44 lol
when Investigate runs Claude Code on my machine, do logs with secrets in them go to the model as is??? or is there some redaction before the agent sees them???
@thamibenjelloun Thanks, yeah it was important for us to be transparent. Too many benchmarks out there that no one knows how legit they are.
As for your question - yes there's a redaction engine that scrubs anything secret-looking (and of course the actual k8s secret values)
Congrats on the launch. What all have you added lately to radar?
@pritesh_kumar3 thanks Pritesh! we actually added so many things but figured we'd focus the attention now for this launch on the MCP + AI investigations. Under the hood same engine helps engineers using the UI and agents using MCP, and there's a layer of optimization for how agents work that we found really makes a huge difference, much more than people expect.
The SREGym link I shared shows how much faster radar has become at finding root cause (well, your generic agent using radar) which is maybe the most important thign users want from radar - help fix production...
Read-only investigation with evidence for each claim is a good call. I'd be much more comfortable letting an agent investigate production issues that way. Also, the change timeline sounds especially useful. Congratulations!
@henry_habib thanks!
yes we put an emphasis on read only + evidence backed.
a lot of people still worried about giving agents access to their production - just need the right tools to do it safely
The change timeline is the part I'd look at first. Seeing what changed just before a workload failed gives the investigation somewhere to start.
@oleksii_sekundant thanks - one of the key differentiators from tools that don't use it well enough
Fresh news: Radar is now #1 on SREGym benchmark: https://sregym.com
And it's not even close 😅