Launching today

Cloptima
AI Gateway, Guardrails & LLM FinOps
8 followers
AI Gateway, Guardrails & LLM FinOps
8 followers
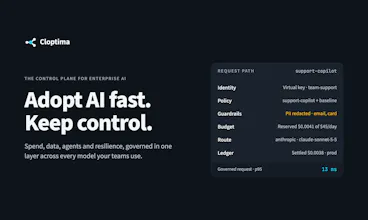
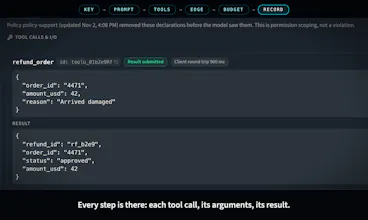
Cloptima puts your own rules in front of every AI call: a virtual key per app with its own policy, guardrails that mask data before it leaves, tool policy for agents, budgets that block, session replay, an edge gateway inside your network, and prices each call on an attributed ledger before the provider sees a token. Setup is one line.




Free Options
Launch Team

CloudflareYour next app belongs on Cloudflare Workers. Deploy for free
Promoted
Hi Product Hunt 👋 I'm Rahul, Founder of Cloptima.
Why I built it: AI calls go straight from app code to a model provider, while the rules a company actually cares about (what it may spend, which data may leave, which tools an agent may use) live in a policy document, not in the request path. So teams either slow down to review everything by hand, or ship and find out later. I wanted those rules to run on every call, before it leaves, without asking developers to rewrite anything.
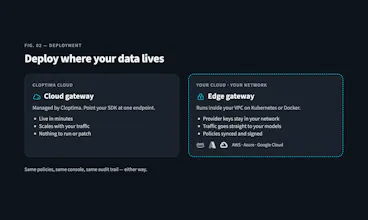
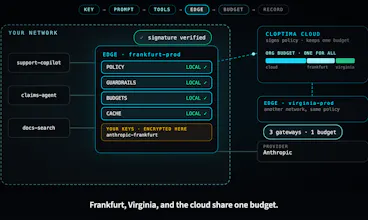
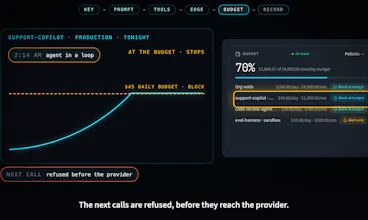
What's in it today: a key per app, guardrails that mask data before it leaves (and can watch first before they block), tool policy for agents, budgets that block at the line, session replay, and an edge gateway that runs inside your own network. Setup is changing your client's base URL to get started, and then enrich with further attributions.
Feedback that would help most:
Where would this get in your way? A wrong block costs you more than a missed one, so tell me where the defaults feel heavy.
What would you need to see before you put production traffic through a gateway?
If you run agents: which tool or session controls are missing?
It's free to try, no credit card, and for launch day: sign up with Google or Github and get $20 in credits, 30 slots open today.
The watch-before-block option is a useful way to introduce a new rule. Seeing the requests it would have stopped, with the reason for each, would make the decision to enforce it easier.
@oleksii_sekundant You can add this feedback as a Hypership suggestion! Just scroll up and click the "New request" button
Thanks! That's the part that makes people trust a new rule. It's already in there: in monitor-only mode, every request the policy would have blocked shows up in Audit with the reason, and you can open each one. And you can switch the policy to Enforce mode with one click when ready.