Launching today

Vallkey
Spending caps and a kill switch for every API key
0 followers
Spending caps and a kill switch for every API key
0 followers
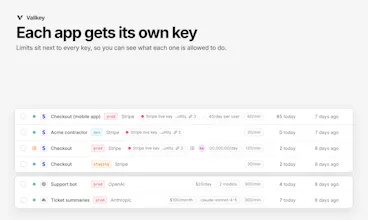
A leaked API key can run up a huge bill before you notice. Vallkey keeps your real keys out of your code and gives each app a stand-in key with its own rules: spending caps, AI budgets, allowed endpoints and models. If a key leaks, it can only do what you allowed. See every request, get told when a key shows up somewhere new, and kill any key in one click without touching the real one. Works with 196+ services, including Stripe, OpenAI and Anthropic.




Free Options
Launch Team

AWS Startup AdvisorPersonalized AWS guidance that meets you where you’re already building
Promoted
Hi Product Hunt, I'm Mokhtar. I built Vallkey because it bothered me that one leaked API key could do everything the real account can.
Most apps run on real API keys with full access. Those keys get copied into env files, logs and old repos, and when one leaks you usually find out from the bill.
With Vallkey, your real key stays out of your code. Each app gets a stand-in key that only works within the rules you set. You can give it:
- Spending caps and AI budgets
- A list of allowed endpoints and models, so a checkout key stays a checkout key
- Alerts when it shows up in a new country or network
- A kill switch that stops that one key, while your real key and other apps keep working
It's a good fit if you ship with OpenAI, Anthropic or Stripe, or if you run AI coding agents and don't want them holding your real keys. There's also an audit log for teams and short-lived keys for browsers and mobile apps.
You can check a project for exposed keys right now, with no account:
npx vallkey scan
When you're ready, npx vallkey init swaps your keys and npx vallkey connect sets up your app, usually with no code changes. It works with Node.js, Bun, Python, Ruby, Java, .NET, PHP and Elixir.
I'd really like to hear from you: what would stop you from using this on a real project?