Launching today

StackLégal
GDPR docs whose DPA names your real sub-processors
2 followers
GDPR docs whose DPA names your real sub-processors
2 followers
Tick your SaaS tools and get a privacy policy, terms and an Art. 28 DPA naming your real sub-processors. Free: cookie-before-consent scanner, sub-processor widget, JSON API + MCP. 73 vendor fiches, 22 languages. Pay once from 19 €.



Free Options
Launch Team

Customer.ioAutomate Messaging Everywhere — Startups Get 12 Months Free
Promoted
Hi Product Hunt 👋 I'm Corentin, solo maker from France.
Every SaaS selling to European businesses eventually gets: "can you send your DPA and sub-processor list?" Cheap generators say "our trusted partners". Procurement wants Vercel, Stripe, Supabase — named, with where data goes.
StackLégal: tick the tools in your stack, the documents name only those vendors.
Free, no account:
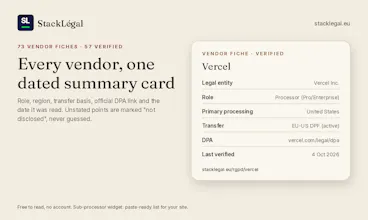
• 73 vendor fiches (57 verified): DPA link, location, transfer basis, date read. Unstated = "not disclosed", never guessed.
• Cookie scanner: flags cookies/trackers already set before consent (first HTTP response).
• Sub-processor widget: paste-ready list for your site.
• JSON API + MCP server (official MCP registry: eu.stacklegal/catalog) so Claude/Cursor can query the catalog.
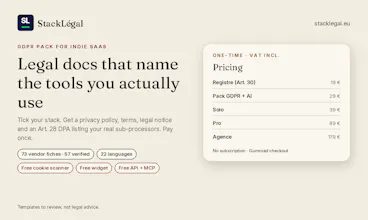
Paid, one-time (Gumroad, VAT incl.): Register (Art. 30) 19 € · GDPR + AI pack 29 € (DPIA template, AI-provider clauses, transparency notice) · Solo 39 € · Pro 89 € · Agency 179 €.
Built in public: it went live two weeks ago, and Product Hunt is its first real launch, so honest feedback helps a lot. Built with heavy help from AI agents; every vendor fact links to the vendor's own page. These are templates to review, not legal advice — I'm not a law firm. 22 languages, but only the French version is tuned to national law (CNIL/LCEN).
What I'd love: which tool is missing? Any fiche line wrong? Does the DPA annex read like what your B2B customers expect?
Thanks / merci !