Launching today

CSP Evaluator API
Find the weak spots in a Content Security Policy.
1 follower
Find the weak spots in a Content Security Policy.
1 follower
Statically evaluates a Content Security Policy against W3C CSP Level 3 and returns one graded JSON report. GET /v1/check fetches a page and reads the Content-Security-Policy and Report-Only headers plus meta tags; POST /v1/validate takes policy text directly. Returns a verdict (enforced, report_only, no_csp, ineffective), scriptProtection (strict, allowlist, none, unknown) and issues with stable codes and spec links. A static assessment, not proof of safety.

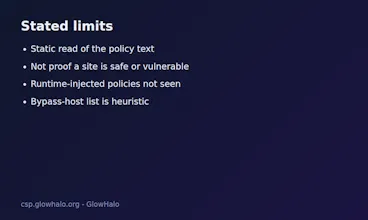


Hi, I built this so a CSP can be graded in CI or an audit tool without parsing it by hand. Comma-separated policies are evaluated separately, and Report-Only findings are listed one level lower and kept out of the score when an enforced policy exists. Limits are in the docs: it is a static read of the policy text, so a clean report is not a security guarantee, it cannot see policies injected at runtime, and the bypass-host list is heuristic. Feedback welcome.