Launching today

AWS Bedrock Guardrail Firewall
Privacy-first guardrails for generative AI
1 follower
Privacy-first guardrails for generative AI
1 follower
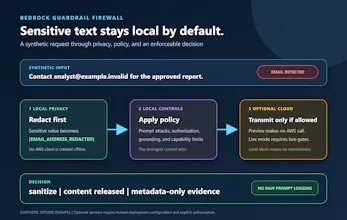
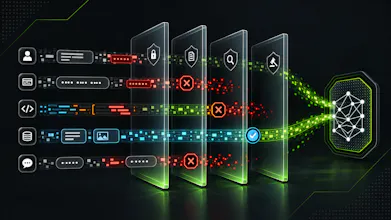
Bedrock Guardrail Firewall is an open-source, privacy-first policy enforcement layer for generative AI. It redacts sensitive data locally, detects prompt attacks, checks grounding and authorization, and can optionally call Amazon Bedrock Guardrails or Microsoft Presidio. Offline by default, fail-closed in production, and backed by metadata-only, tamper-evident audit trails.

Free
Launch Team

CloudflareDeploy serverless functions globally in seconds
Promoted
I built Bedrock Guardrail Firewall because teams adopting generative AI need enforceable controls around prompts and responses without automatically sending sensitive content to another cloud service.
The core runs locally and offline by default. It redacts PII, detects prompt injection, checks authorization and grounding, applies the strongest policy decision, and releases content only when the result is allow or sanitize. Optional Presidio and Amazon Bedrock Guardrails integrations are separately gated and verified; production mode fails closed when required controls are unavailable.
The project is open source under Apache 2.0, packaged on PyPI, and includes 218 tests, an adversarial suite, tamper-evident metadata-only auditing, SBOMs, provenance, and reproducible release evidence.
I’d especially value feedback on the policy profiles and decision model, the offline onboarding experience, and the controls or integrations security teams would need before piloting it. You can try the core without AWS credentials or network calls. Thanks for taking a look!