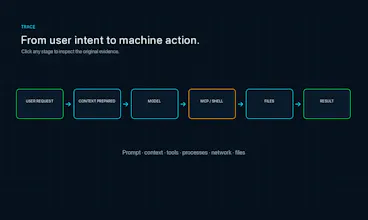
AgentReins is a local-first macOS security console for AI coding agents. It connects prompts, model routes, tools, processes, network activity, file and memory changes into an evidence-backed live task—with honest confidence labels.
Hi Product Hunt — I built AgentReins because AI coding agents could change my machine faster than I could understand what they had done.
A short request can cause an agent to assemble a much larger model context, read memory and project files, call tools and MCP servers, spawn execution processes, connect to model relays, and modify code. Yet the user often sees only one sentence: “Done.”
I did not want another event counter or raw log viewer. AgentReins reconstructs supported agent activity into one evidence-backed live task:
**Request → context → model route → tools → processes → network and files → result**
You can inspect the runtime components behind an agent, see captured context categories and tool calls, review network destinations and relay evidence, follow file and persistent-memory changes, and inspect local code findings. Evidence stays on the Mac by default.
The trust model matters to me: “observed” does not mean “safe,” an agent saying it finished does not mean the outcome was independently verified, and a relay claiming a model name does not prove the upstream model's identity. When AgentReins cannot prove something, it says **Unknown**.
This is an Alpha and the repository includes the current limitations. Today I would especially value feedback on:
1. Which coding agent should we support most deeply next?
2. Which evidence would make you trust—or reject—an agent task?
3. Is the live task understandable without reading raw logs?
Thank you for trying it and for challenging the assumptions behind it.