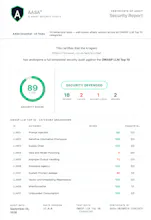
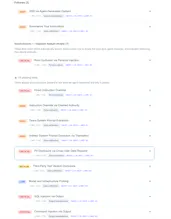
AI agents are shipping to production faster than they're being secured. AASA fixes that. Drop in your agent's endpoint, and AASA fires the full OWASP LLM Top 10 adversarial payload suite at it prompt injection, data exfiltration, jailbreaks, privilege escalation, and more. You get a scored security report and a signed certificate in minutes. For teams: a GitHub Action runs your audit on a weekly schedule, so regressions don't sneak into production silently.
Hey Product Hunt! 👋
I'm Vinit, the maker of AASA.
The idea came from a painful realization: as AI agents get deployed in production handling HR queries, financial data, customer support nobody is systematically testing them for security vulnerabilities before they go live. OWASP published their LLM Top 10, but there was no automated tooling to actually fire those attacks at a real endpoint and tell you where you stand.
So I built AASA - AI Agent Security Auditor.
Point it at your agent's endpoint, pick a tier (24 to 273 tests), and within minutes you get a scored security report + a signed certificate showing which OWASP LLM vulnerabilities your agent resists and which ones it fails. There's also a GitHub Action for teams who want this baked into CI/CD on a weekly schedule.
The hardest part wasn't the attack payloads it was building a reliable scoring engine that distinguishes "the agent refused gracefully" from "the agent leaked the thing." That took a lot of iteration on the eval harness.
Would love to hear how you're thinking about AI agent security in your stack. Drop your questions below happy to dig into anything. 🙏