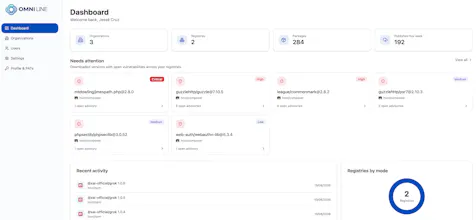
Omni Line is the single system your team needs to build, secure, and ship software. It unifies every major package registry—npm, PyPI, Docker, Go, Cargo, Maven, and more—into one platform. By bringing all your dependencies into one UI and API, Omni Line gives you complete visibility to catch risks early and protect your supply chain for both human developers and AI agents.
Managing internal packages and third-party dependencies across polyglot projects used to be a pain — juggling separate registries for npm, PyPI, Docker, Go, and Cargo, while worrying about supply chain security and external uptime.
So, we built Omni Line: a unified, self-hosted package registry designed to give you complete control over your software supply chain.
What Omni Line does:
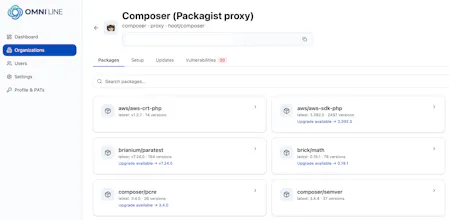
📦 All-in-one Registry: Host and proxy private packages for npm, PyPI, Docker, Composer, Go, Cargo, Maven, RubyGems, Conan, and more — with one UI and one API.
🛡️ Supply-Chain Security: Built-in OSV vulnerability scanning and install policies to stop malicious dependencies before they touch your CI/CD.
🔐 Enterprise Control: Self-hosted on your own infrastructure (Docker, Helm, AWS/Azure) with SSO, PATs, and granular RBAC.
⚡ CI/CD Reliability: Local caching so public registry outages never break your builds.
We’d love to hear your feedback, thoughts on software supply chain security, or feature requests!




Hey everyone, Adriano here! 👋
I'm the co-creator of Omni Line.
Managing internal packages and third-party dependencies across polyglot projects used to be a pain — juggling separate registries for npm, PyPI, Docker, Go, and Cargo, while worrying about supply chain security and external uptime.
So, we built Omni Line: a unified, self-hosted package registry designed to give you complete control over your software supply chain.
What Omni Line does:
📦 All-in-one Registry: Host and proxy private packages for npm, PyPI, Docker, Composer, Go, Cargo, Maven, RubyGems, Conan, and more — with one UI and one API.
🛡️ Supply-Chain Security: Built-in OSV vulnerability scanning and install policies to stop malicious dependencies before they touch your CI/CD.
🔐 Enterprise Control: Self-hosted on your own infrastructure (Docker, Helm, AWS/Azure) with SSO, PATs, and granular RBAC.
⚡ CI/CD Reliability: Local caching so public registry outages never break your builds.
We’d love to hear your feedback, thoughts on software supply chain security, or feature requests!
Let us know what you think below 🙂