Launching today

SniffPup
Free outside-in security check for AI-built web apps
2 followers
Free outside-in security check for AI-built web apps
2 followers
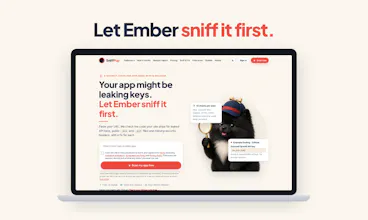
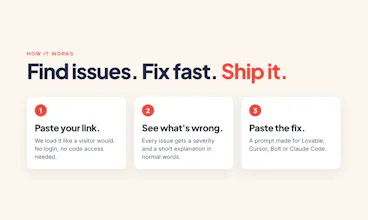
Paste your live URL. SniffPup passively checks web apps built with Lovable, Bolt, Cursor, Replit or Supabase for leaked keys, publicenv/.git files, source maps, missing headers and open Supabase/Firebase reads. Read-only. Every critical fix is free.



Free Options
Launch Team

CloudflareYour next app belongs on Cloudflare Workers. Deploy for free
Promoted
Hi Product Hunt, I'm Garrett. I build a lot of apps with AI tools like Lovable, Bolt and Cursor. SniffPup is named after Ember, my black Pomeranian. She's the real dog in the logo, and she notices everything.
Building that fast makes it easy to ship a secret key in your JavaScript, a public /.env file, or a Supabase table a stranger can read, without noticing. The builders' own security checks are good, and I'd run those first. I built SniffPup to add the outside view: it looks at your live URL the way a stranger's browser does.
What it checks, all from the outside: leaked keys in your page and JS bundles, exposed files like .env and .git, public source maps, security headers and cookies, your HTTPS certificate, CORS, email DNS, and whether Supabase or Firebase lets an anonymous visitor read data.
What it doesn't do:
- It's a passive, read-only outside scan. It never logs in, sends attack payloads or uses a key it finds, so it's not a pen test or a code audit.
- It only scans public web URLs, not native iOS or Android apps.
- A score of 100 means our checks found nothing. It isn't proof your app is secure.
The scan needs no signup. Please only scan sites you own.
I'd really like your feedback: what's one thing you'd want it to check on your app that it doesn't today? 🐾