Launching today

Flare AI
Cloud and SaaS audit investigations for vibe-coded teams
4 followers
Cloud and SaaS audit investigations for vibe-coded teams
4 followers
Shipping a vibe-coded project? Flare AI helps small teams investigate who gained access, what changed, and what needs attention in cloud and SaaS audit logs. Review findings and source evidence for AWS and Google Cloud, with Google Workspace and GitHub Enterprise Cloud audits in early access. Try the sample and help shape Flare as an early tester.


Free
Launch Team

Atlassian LoomShow, don't just tell with Loom
Promoted
Hi everyone! I built Flare for small teams and builders shipping vibe-coded projects who need to understand what is happening in their cloud and SaaS environments.
AI can help you ship quickly, but you still need to investigate who has access and what changed. I want useful, lightweight SIEM capabilities to be accessible without a dedicated security team. I believe detection should pay more attention to changes in behavior, alongside predefined rules.
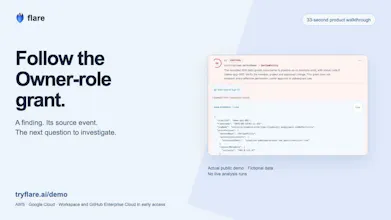
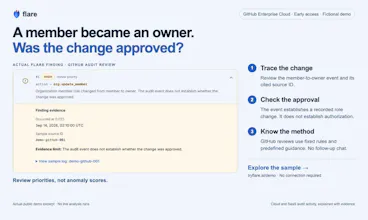
A service account receives Owner access. Was it approved? What does the audit event actually prove, and what still needs checking? That’s the investigation our public sample walks through.
Today, Flare brings ranked findings and supporting evidence together for AWS and Google Cloud, with Google Workspace and GitHub Enterprise Cloud audit reviews in early access. Capabilities vary by source: GitHub reviews use deterministic rules and don’t offer follow-up chat.
Try the sample without connecting an account: https://tryflare.ai/demo
It uses fictional records and scripted replies, so you can explore the workflow without sharing your logs.
If you’re shipping a vibe-coded project, I’d love your help testing Flare. Tell me which cloud or SaaS services you use and one access or activity question you struggle to answer. If you would join a short sample walkthrough, say so too. We can start with fictional data; no production logs or credentials needed.