Launching today

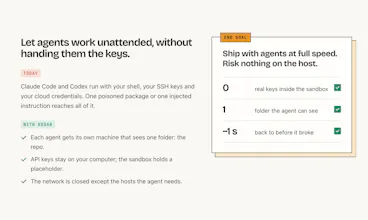
AI coding agents need a real machine to be useful, but giving them yours means handing over your keys, files and network. kosa8 gives every agent its own sealed VM that sees one folder, keeps API keys on the host, and blocks outbound traffic except allow-listed hosts. Snapshot and rewind in about a second, fork up to 8 live copies, and keep a tamper-evident audit log. Docker-compatible, and runs Claude Code, Codex and Gemini with one command.



Free Options
Launch Team / Built With


AWS Activate CreditsCredits that fuel your startup’s next milestone
Promoted
Hey Product Hunt 👋 I'm Drew, maker of kosa8.
I started building it after watching coding agents run with my shell, my SSH keys and my cloud credentials. One poisoned package or one prompt injection, and an agent can reach all of it. Containers share the host kernel, so I wanted a real wall without the usual VM slowness.
kosa8 gives every agent its own sealed machine:
• It sees one folder (usually the repo), nothing else
• API keys stay on your computer; the sandbox only holds a placeholder
• The network is closed except the hosts you allow
• Save, copy and rewind a running machine in about a second when the agent gets it wrong
• Every action lands in a tamper-evident audit log
It's Docker-compatible, so your CLI and Compose files work as-is, and kits run Claude Code, Codex and Gemini with one command. Runs on Apple-silicon Macs, Linux and Windows 11 (WSL2, preview). Try it free for 14 days, no card or account needed.
I'd love your feedback: what's the first agent you'd put in a sandbox, and what would stop you from using kosa8 today? I'll be here all day answering questions.