Launching today

Varaxon Scan Hub
Turn vulnerability scans into client-ready reports
1 follower
Turn vulnerability scans into client-ready reports
1 follower
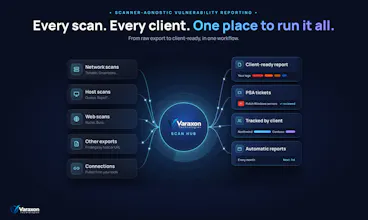
Upload an export from Nessus, Qualys, Rapid7, Greenbone/OpenVAS, Nuclei or another vulnerability scanner, or connect Microsoft Defender. Scan Hub ranks every finding by real-world exploitation (CISA KEV, EPSS) and writes a branded, plain-English report your client can act on. Built for MSPs, MSSPs and consultants. Free pre-flight check, no account needed. First 3 reports free.



Free Options
Launch Team

MailChannels Email APISend transactional email with tenant-level abuse control
Promoted
Hey Product Hunt, I'm Brandon, founder of Varaxon. I built Scan Hub because writing vulnerability reports for clients is the part of security work nobody enjoys. A scanner export is thousands of rows sorted by CVSS, but the client just wants to know what's actually dangerous and what to fix first. Scan Hub reads the export (or pulls from Microsoft Defender or ConnectSecure), checks every finding against CISA's Known Exploited Vulnerabilities list and EPSS, and writes a branded report in plain English. It also never shows missing data as a clean result. Try the free pre-flight check with one of your own exports: no account needed, and the file isn't stored. I'd love your feedback: what would make this a no-brainer for your team?